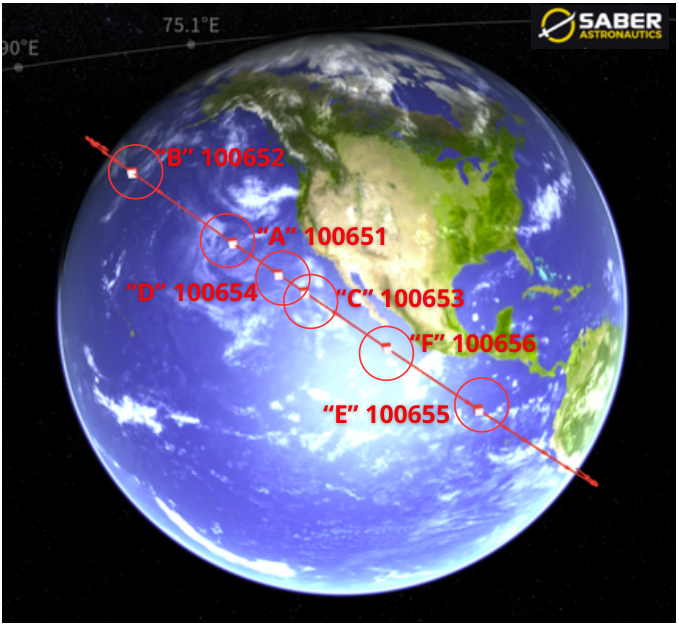
25 Sep 2026: In Issue 153 we reported China's 10 September Long March-4B launch of six satellites, 3x Yaogan-53 and 3x Yaogan-56, into 518km circular orbits inclined 45°, and noted it was unknown whether the group would maneuver into some s
25 Sep 2026: In Issue 153 we reported China’s 10 September Long March-4B launch of six satellites, 3x Yaogan-53 and 3x Yaogan-56, into 518km circular orbits inclined 45°, and noted it was unknown whether the group would maneuver into some sort of formation. Two weeks of orbital data reveals that all 6 satellites have maneuvered and China is beginning to disperse them, likely in-plane. We don’t know what the final formation will look like…yet.
There’s quite a bit we still don’t know, first of all which satellites are YG-53 versus those that are YG-56: the six payloads remain cataloged only as Objects A through F (SATNOs 100651-100656). We therefore refer to each object by its catalog name and SATNO throughout.
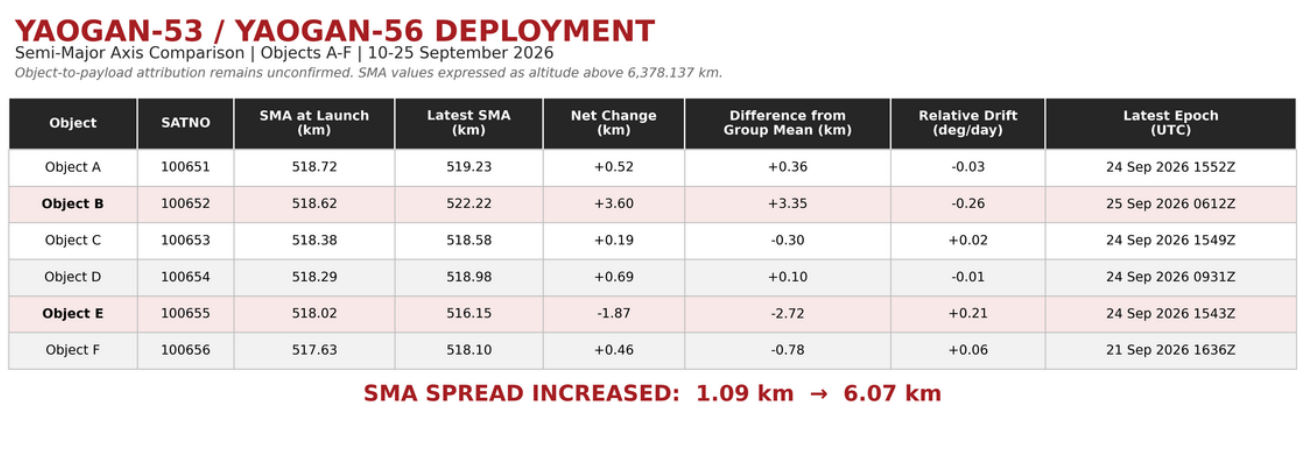
At launch all 6 objects were tightly clustered, with a total semi-major axis (SMA) from 517.6 – 518.7km altitude (1.1km spread). All objects were (and continue to be) co-planar with equal inclination and RAAN values. As of 24-25 September the SMA spread has grown to ~6.1km, achieved through a series of small in-track maneuvers between 14 and 21 September.
Maneuver Summary: Object B (100652) is a clear outlier: after minor maneuvers on 14-16 September it executed a single large orbit raise between 17 and 21 September, lifting SMA ~4.1km to 522.3km. Object E (100655) went the opposite direction, lowering SMA ~1.25km on 16-17 September and trimming again around 21 September to settle at 516.2km, the lowest of the six. The remaining four — Objects A (100651), C (100653), D (100654) and F (100656) — performed small SMA raises of 0.2 to 0.7km, keeping them clustered within ~1km of one another near 518.1-519.2km. As a result (see 10:1 rule) Object B now “trails” the other 5 satellites with Object E in the lead.
It looks like China is slowly phasing the 6 satellites and intends to keep them co-planar, unlike what we will likely see with YG-40 (more on this later). With the differing SMA values China is slowly walking the objects apart to establish a phased, string in a single plane, similar to prior Yaogan formation (YG-35/36/39/43) build-outs. We’ll know for certain if/when China equalizes the all of the satellites’ SMAs.
24 Sep 2026: China launched a Long March-6A with 3 satellites comprising the Yaogan-40 04 formation (100823-100825) from Taiyuan. As the name implies this is the 4th set of YG-40s, all have used the LM-6A and were launched from Taiyuan. For
24 Sep 2026: China launched a Long March-6A with 3 satellites comprising the Yaogan-40 04 formation (100823-100825) from Taiyuan. As the name implies this is the 4th set of YG-40s, all have used the LM-6A and were launched from Taiyuan. For a nominal deployment we’ll see one of the satellites orbit at a lower altitude for 6-8 weeks to establish a west RAAN offset with the other two. Then Chinese space operators will raise the orbit of the third satellite to create an equilateral triangle formation. This formation is typically used to support collection and geolocation of electronic signals. According to official sources, the satellites entered the preset orbits and “will be used to carry out electromagnetic environment detection and related technical tests”. Launch Video.
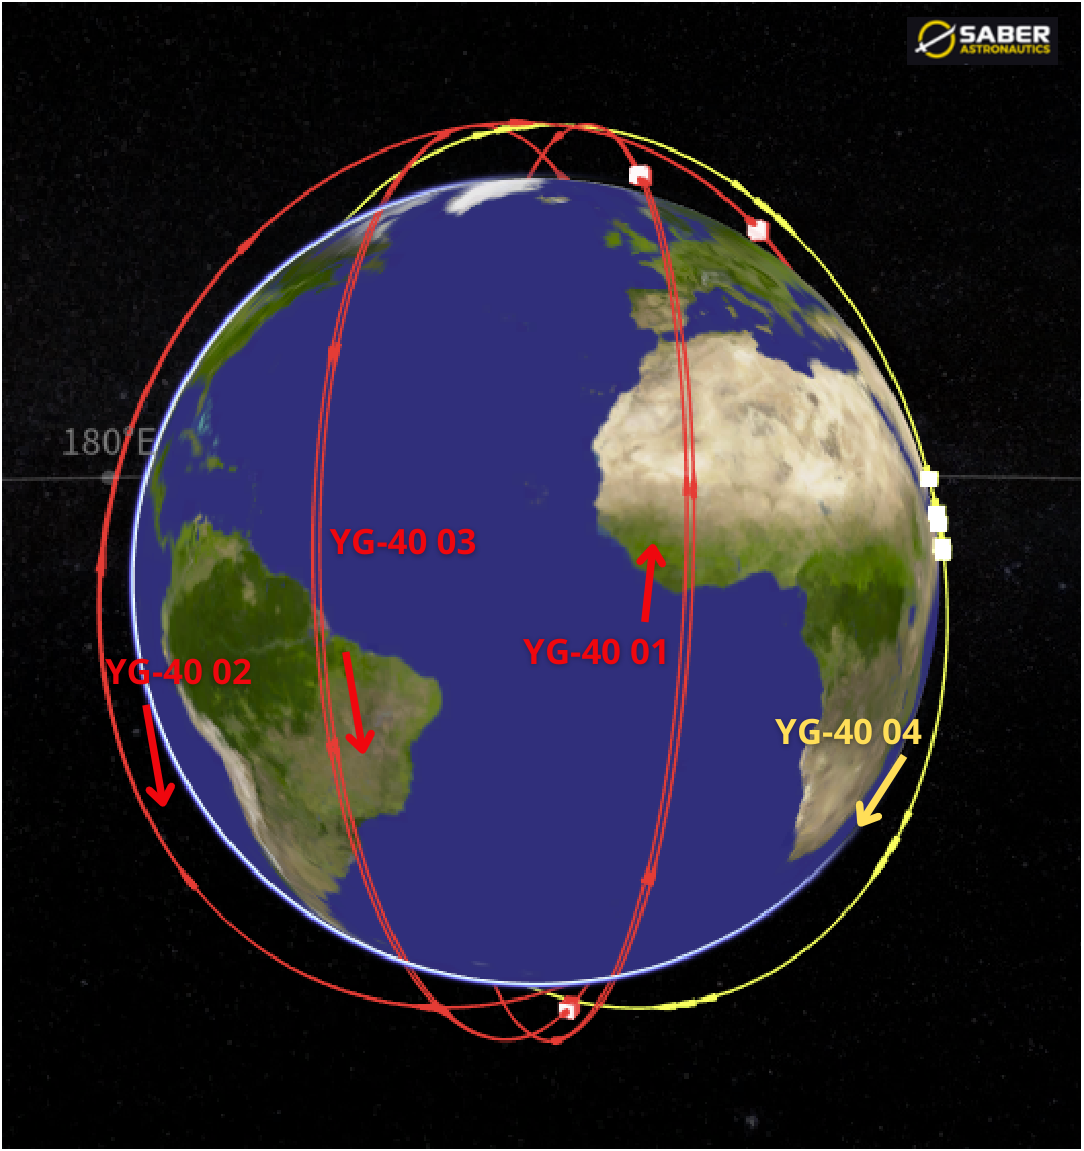
YG-40 Launch Dates (all from Taiyuan using LM-6C):
Each deployment has followed nearly the same sequence. Two satellites climb from their ~802 km insertion orbit to the 851 km operating altitude. Meanwhile, the third satellite (the “singleton”) drops to ~785 km and drifts west until it’s about 0.75° of RAAN away from the pair, then climbs to join them. The pairs reached operating altitude 12 and 17 days after launch in both the 02 and 03 deployments. YG-40 01 took about 60 days to complete its triangle formation in late 2023. YG-40 02 snapped into formation 66 days after launch, when 02C was raised 8–16 Jul 2025. YG-40 03 took 62 days, with 03A (65547) completing its climb in early November 2025. The YG-40 04 satellites are still near their insertion altitude. If China follows the same template, the fourth formation should take shape in late November 2026.
It appears China intends for the Yaogan-40 constellation to consist of five orbital planes spaced about 72° apart in RAAN. YG-40 04 launched into the orbital plane between the YG-02 and 03. That leaves one open slot: RAAN ≈ 286° (epoch 27 Sep 2026), 72° east of YG-40 01 and 72° west of YG-40 03.
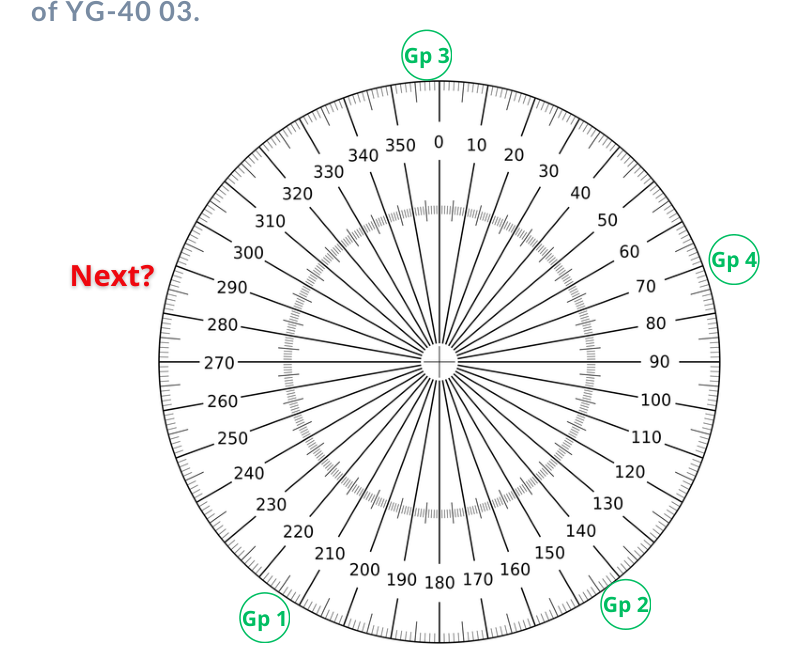
27 Sep 2026: RAAN Values for YG-40 Constellation (based on data from celestrak.org)
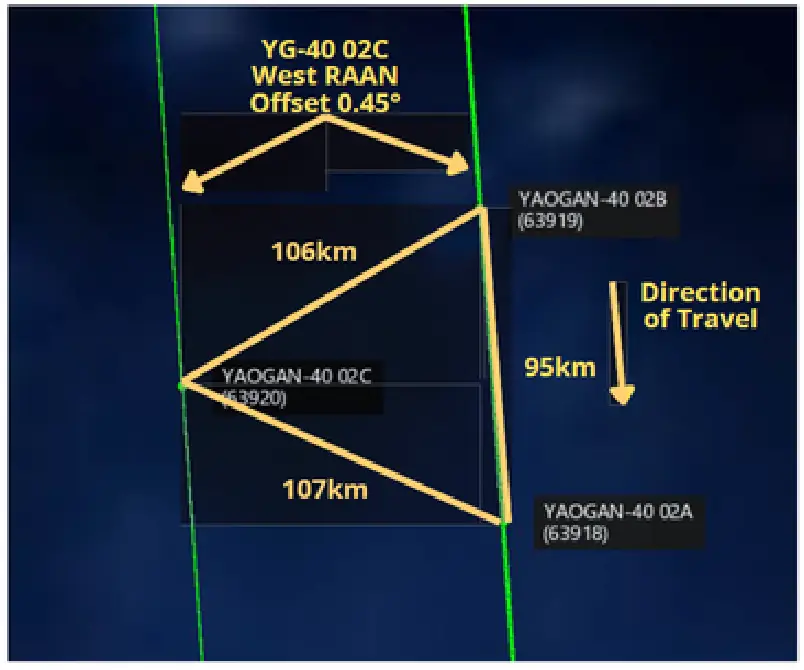
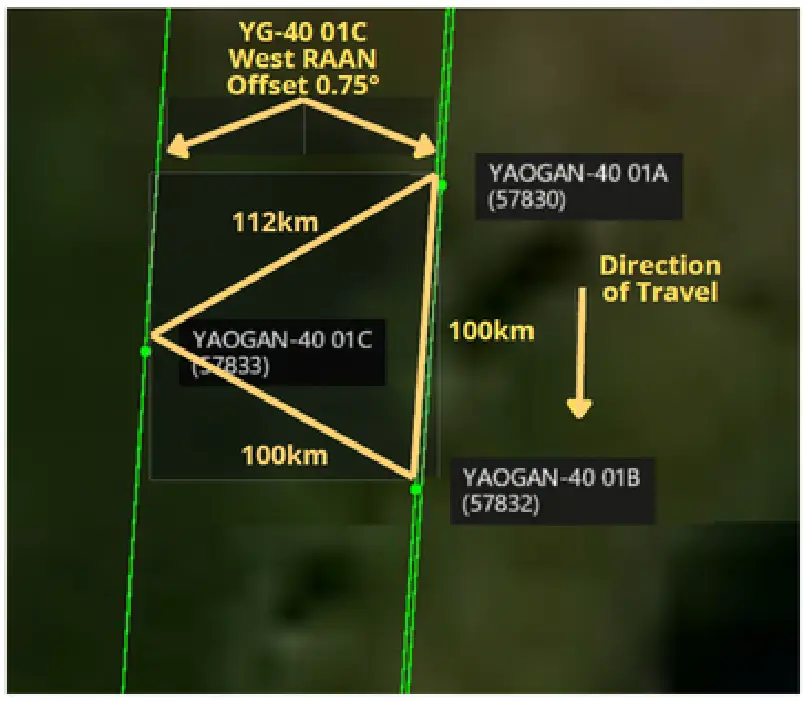
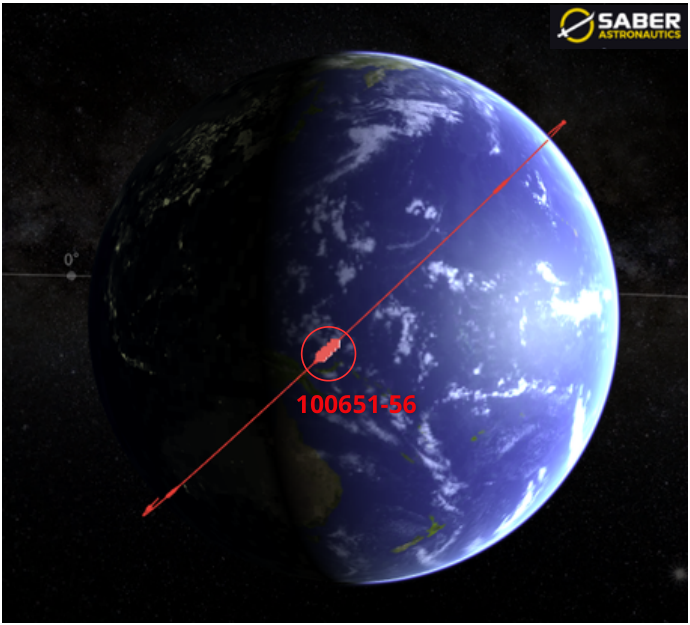
Formation Comparison between YG-40 02 & YG-40 01 equilateral triangle formations as both approach the equator (saberastro.com)
In Issue 153 we reported 43 pieces of debris cataloged from Yaogan-50 02 (68196) and assessed the resulting debris field would be problematic for decades. New analysis published on 19 September by Jim Shell (Friend of the Flash) substantial
In Issue 153 we reported 43 pieces of debris cataloged from Yaogan-50 02 (68196) and assessed the resulting debris field would be problematic for decades. New analysis published on 19 September by Jim Shell (Friend of the Flash) substantially revises that outlook and there is evidence the satellite survived the event.
Jim notes the 43 debris objects appeared in the USSF catalog on 6 September with no prior breakup announcement from either the USSF or commercial space surveillance providers, which has become the norm. The first element sets on the debris were dated 3 September, by which point the cloud was already fully dispersed in-track — and, notably, every object was below the parent. Backward propagation of those element sets converged on a debris event date of ~20 July 2026, consistent with the late-July estimate we cited previously.
Jim also notes Yaogan-50 02 appears to have maneuvered on 10 September 2026, raising its orbit ~100m, and the maneuver is consistent with the satellite’s historical station-keeping pattern. Shell also points out the parent’s altitude history lacks the orbital perturbation typically present in breakup events. His assessment: “this was a very low energy debris event and the Yaogan-50 02 satellite bus appears to still be operating.” Payload health remains unknown.
There is good news on the debris as well. Orbit evolution of the cataloged pieces infers low-mass objects with high area-to-mass ratios. Despite the ~950km near-circular orbit, energy loss has been rapid, and Shell assesses the majority of these objects will re-enter far sooner than initially anticipated. His animated Gabbard plot, spanning roughly 12 days, shows all cataloged debris losing energy relative to the parent with many objects circularizing.
Bottom line: our Issue 153 characterization of a decades-long debris hazard may be overly pessimistic. The event was low-energy, the satellite remains maneuverable, and the majority of the debris should decay relatively quickly. It remains to be seen how many additional objects get cataloged.
Our thanks to Jim Shell for the analysis and graphic. Read his full post at Space Domain Awareness, Orbital Debris, Norms of Behavior.
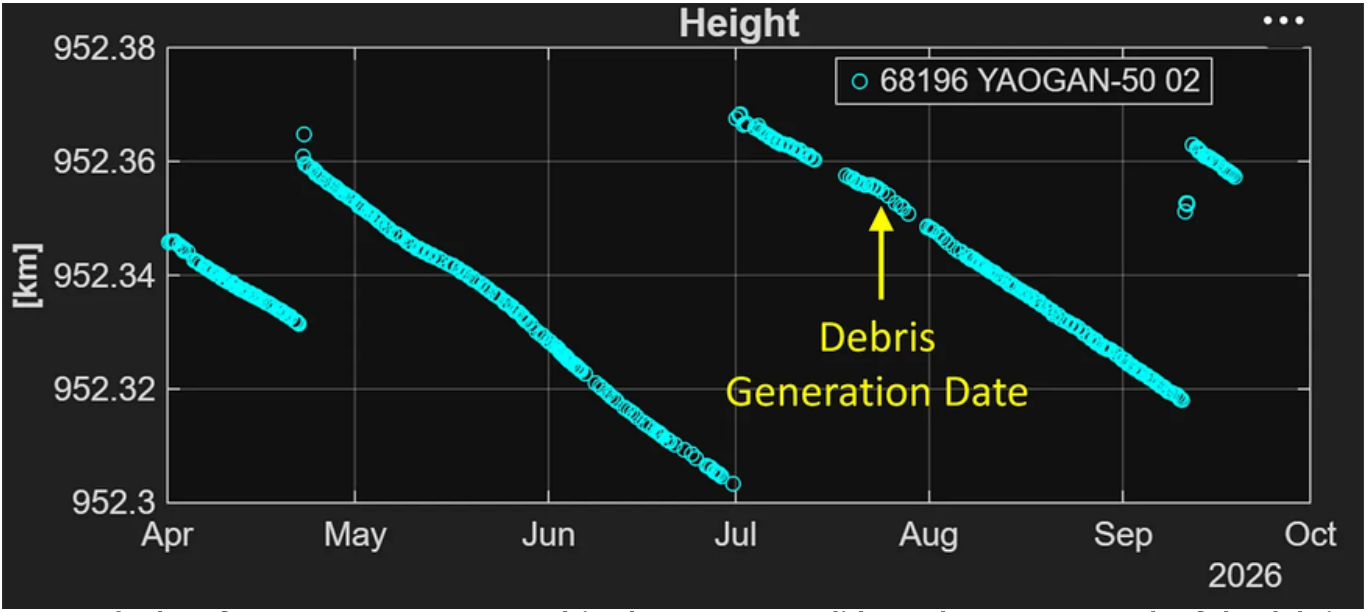
6 Month Plot of YG-50 02 SMA (average altitude). Note SMA did not change as a result of the debris generation event and YG-50 02 maneuvered on 10 September. The manuever raised the satellite’s orbit and is consistent with its pattern of life.
(spacedomain.substack.com)
by Alison Sayer & Greg Gillinger 19 Sep 2026: China launched four PIESAT-2 satellites (PIESAT-2 13-16) (100749-100752) aboard a Long March-2D from Taiyuan. The satellites reportedly carry X-band synthetic aperture radar (SAR), onboard intel
19 Sep 2026: China launched four PIESAT-2 satellites (PIESAT-2 13-16) (100749-100752) aboard a Long March-2D from Taiyuan. The satellites reportedly carry X-band synthetic aperture radar (SAR), onboard intelligent processing, and mission-planning capabilities. According to Chinese reporting, the spacecraft can screen, preprocess, and extract information from remote-sensing data while still on orbit. In theory, this reduces the amount of raw SAR data that needs to make the trip back to the ground and shortens the time between collection and something actually useful coming out the other end. China launched Group 4 into a co-planar orbit with Group 1. Launch Video.
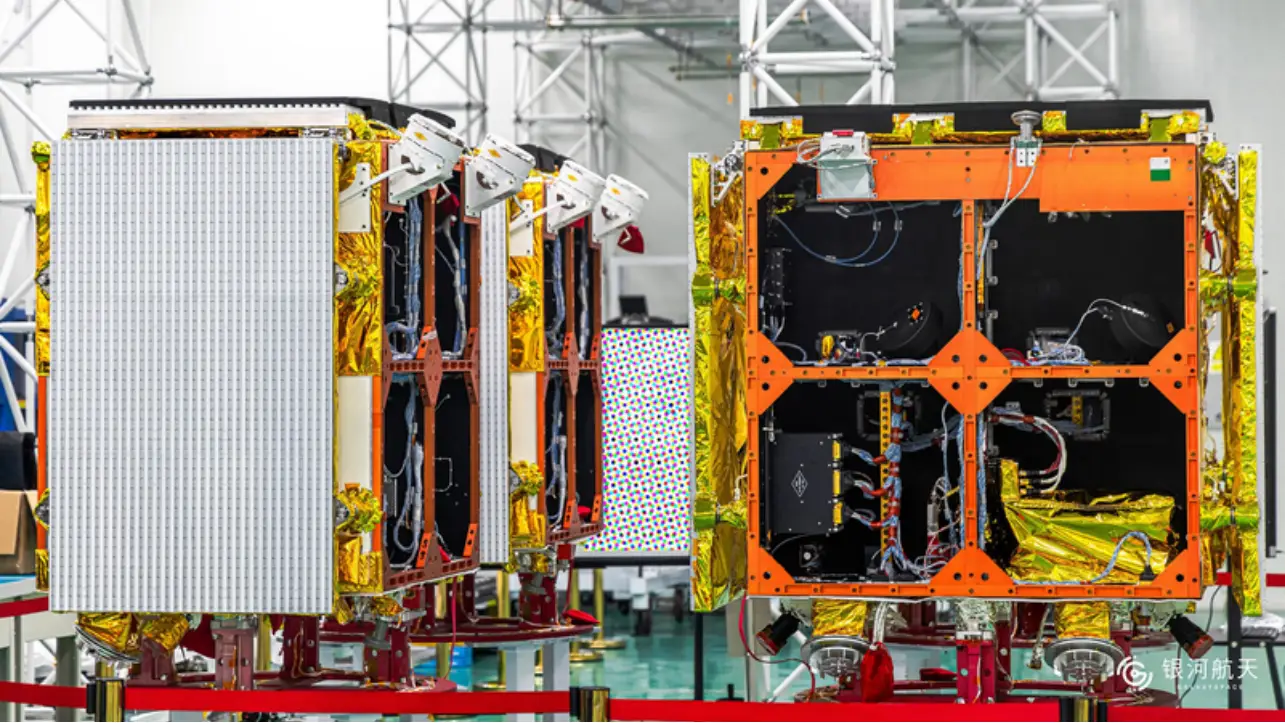
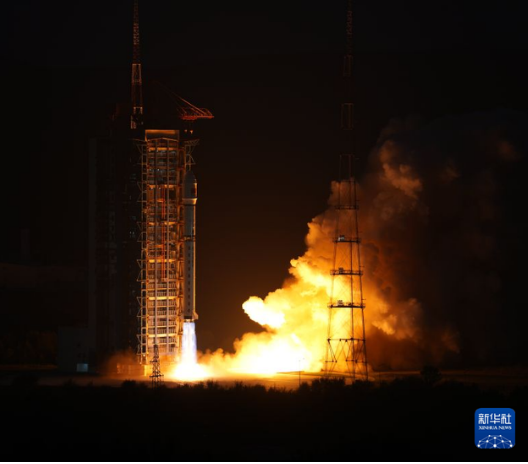
PIESAT-2 Satellites Prepare for Launch Integration (left); Launch from Taiyuan (right).
(nasaspaceflight.com)
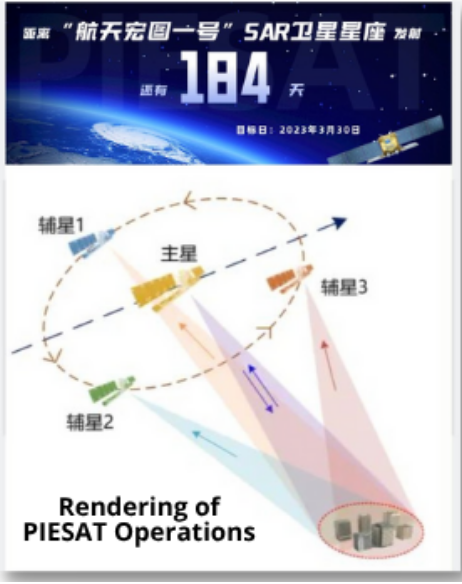
As we previously noted in The Integrity Flash, the Zhuzhou constellation was planned as 16 small SAR satellites operating in four-satellite formations, with the completed architecture expected to reduce revisit time to approximately 2.5 hours. Previous formations used one primary transmitting satellite and three assistant receivers flying in close formation.
Getting to 16 has taken a little more than three years. China launched the original four PIESAT-1 satellites on 30 March 2023, PIESAT-2 01-04 followed on 9 November 2024, and PIESAT-2 09-12 launched just over a month later on 16 December 2024. The latest PIESAT-2 13-16 launch brings the total to 16 spacecraft. Yes, the numbering jumps from 01-04 to 09-12. No, you did not miss a launch. Publicly identified missions do not show a separate PIESAT-2 05-08 formation; the 16-satellite total includes the original four PIESAT-1 spacecraft and 12 PIESAT-2 satellites.
PIESAT Constellation Analysis:
PIESAT’s signature concept is a four-satellite cartwheel (see graphic): one active “pivot” satellite with three passive receivers within ~1 km. Orbital data for all 16 satellites shows only the original PIESAT-1 group is flying that way. Groups 2 and 3 were deployed as distributed, in-plane constellations with each satellite separated by ~90°. The three orbital planes are all 97.5° inclined (sun-synchronous orbit) and have a RAAN offset of ~120°. (see graphic)
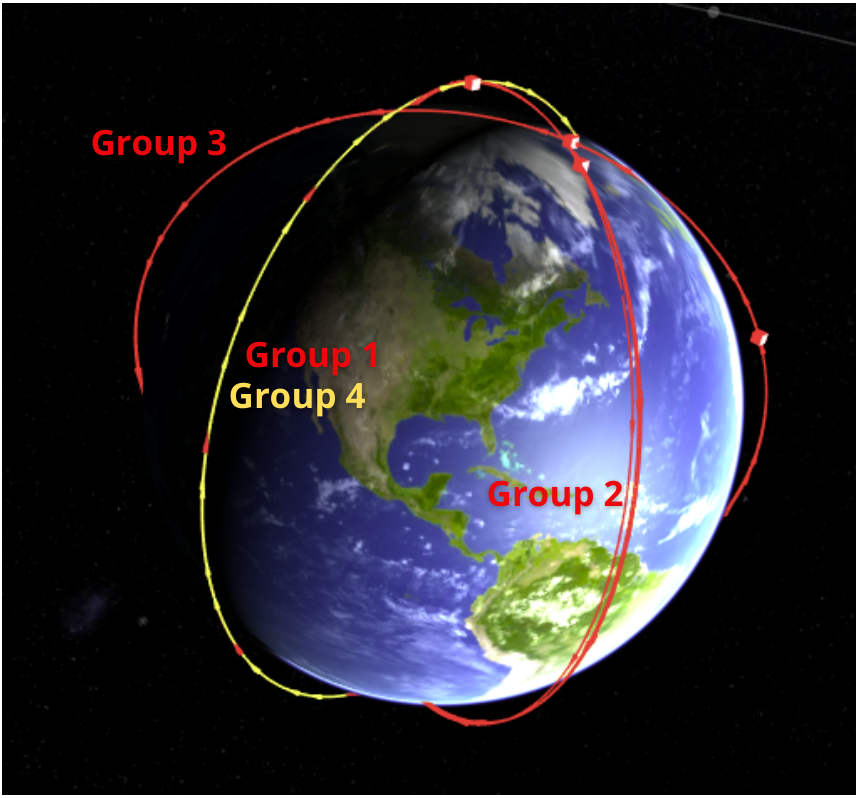
27 Sep 2026: PIESAT Constellation Overview. 3 Sun-Synchronous Orbital Planes separated by 120° of RAAN. Note Group 2 Satellites are beginning to diverge as orbital maintenance has not occurred since April 2025.
(saberastro.com)
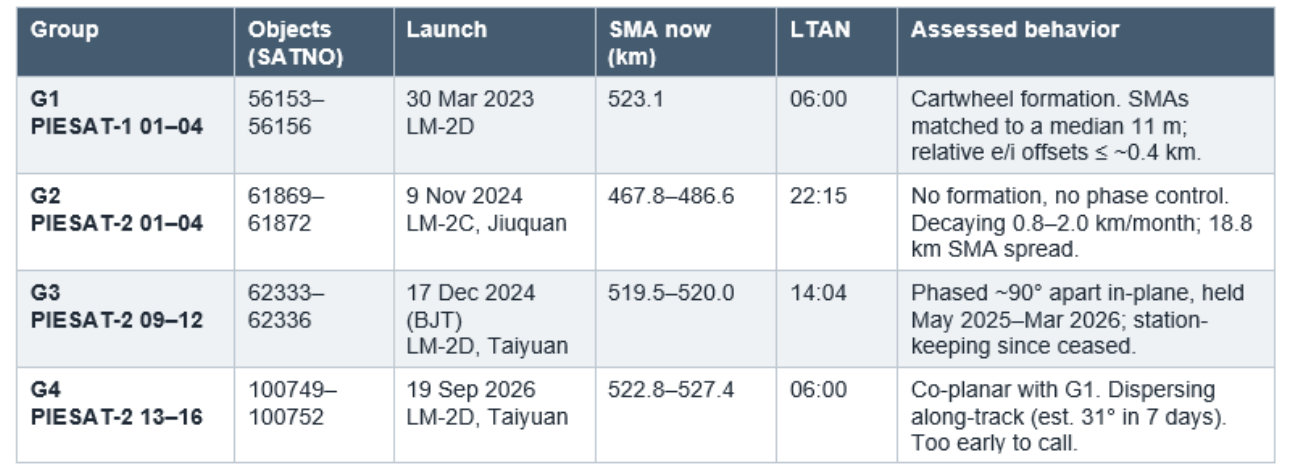
27 Sep 2026: PIESAT Constellation Basics
(based on data from celestrak.org)
While Group 1 (56153-56156) appears to be maintaining its formation (see graphic), the operational status of Groups 2 and 3 is in doubt. Group 2 satellites (61869-61872) may have suffered an anomaly, as they have not maneuvered since April 2025 and it is unclear if they were ever able to reach the desired formation. The four satellites have lost 39–59 km of SMA and now sit at 467.8–486.6 km. 61869 and 61870 are decaying at ~2.0 km/month; 61871 and 61872 at only ~0.8 km/month, which suggests different attitude or drag profiles.
Group 3 (62333–62336) spent Dec 2024 to May 2025 performing large differential SMA maneuvers: 62333 went as high as 532.5 km and 62335 as low as 513.9 km. The four then re-matched at ~525.7 km and held there with routine station-keeping through Mar 2026. The group appears to have stopped station-keeping. All four are decaying together at ~1.1 km/month (now 519.5–520.0 km). 62335 is ~0.57 km higher than the others and is sliding back.
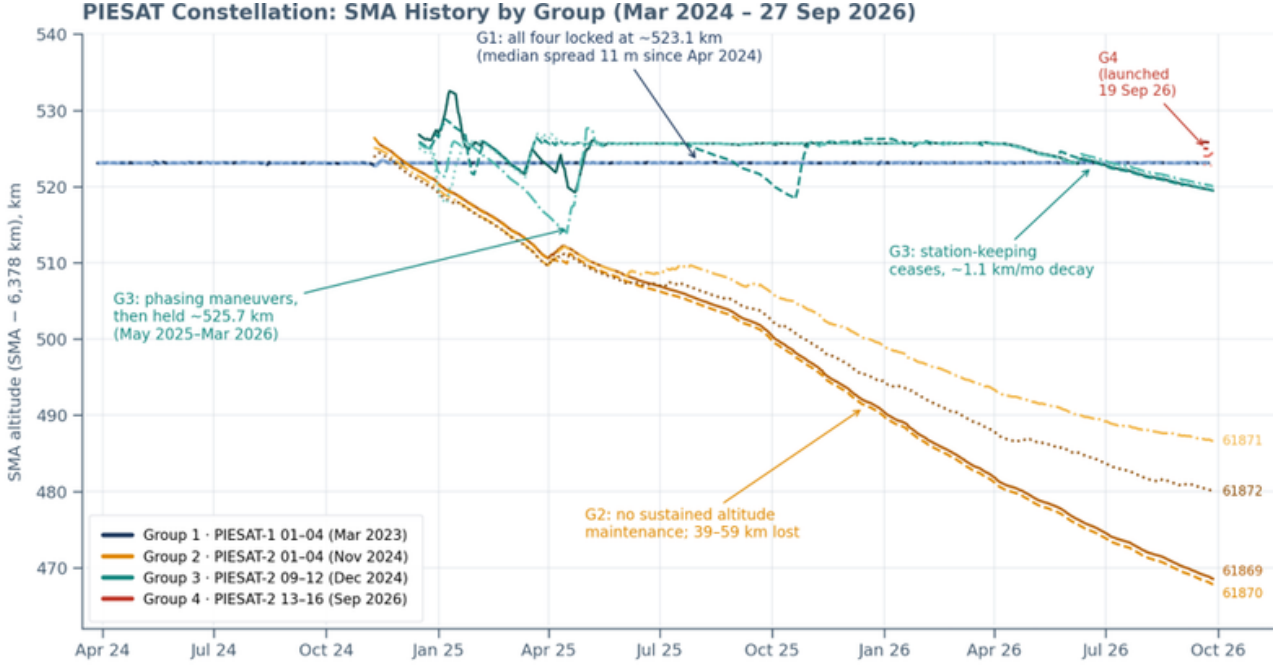
27 Sep 2026: PIESAT SMA Comparisons. Group 1 Appears to be operating nominally, Groups 2 & 3 May have fallen out of formation.
(based on data from celestrak.org)
Initial indications are that PIESAT Group 4 will NOT be replicating Group 1’s cartwheel formation. Early maneuvers are spreading the satellites out. SMA differences has grown from ~3.0 km to ~4.7 km. In their first week alone the 4 satellites dispersed ~3,700km, similar to what we observed with Group 3 in Dec 2024.
Questinable Finances:
The constellation’s unsteady nature is similar to that of its parent company. PIESAT Information Technology Co Ltd was not exactly thriving in August 2025. The company was reportedly dealing with unpaid salaries and supplier bills when it suddenly announced a RMB 990 million contract with an unidentified foreign customer for a satellite and associated ground systems.
A Russian government delegation had visited PIESAT several days earlier. The timing certainly raised eyebrows, but there remains no public evidence identifying Russia as the customer.
Then came another very large contract. In September 2025, PIESAT announced a RMB 2.9 billion agreement with a Pakistani company for a satellite-internet project. Two major foreign deals in a matter of weeks looked, at least on paper, like the kind of thing that could dramatically change the trajectory of a struggling company.
Apparently, paper is doing some heavy lifting there.
PIESAT’s financial problems continued into 2026. The company reported sharply reduced revenue in 2025, and its August 2026 interim report showed first-half revenue falling another 82.5% year-over-year while the company remained loss-making. Several independent directors declined to guarantee the accuracy and completeness of the interim report because issues surrounding the company’s 2025 financial statements, internal controls, and ongoing regulatory investigation remained unresolved. The company itself reported significant uncertainty regarding its ability to continue as a going concern.
Summary:
So we have a somewhat unusual picture. PIESAT the company remains in serious financial trouble, but PIESAT the space system appears to be moving forward. PIESAT operates two concepts under one brand. The Group 1 cartwheel has been held with impressive precision for more than two years. However Groups 2 & 3 which function as a distributed revisit constellation appear to be struggling: Group 2 is effectively uncontrolled and Group 3 has stopped station-keeping. Group 4’s first week points toward the distributed model; we will report again once its SMAs settle.
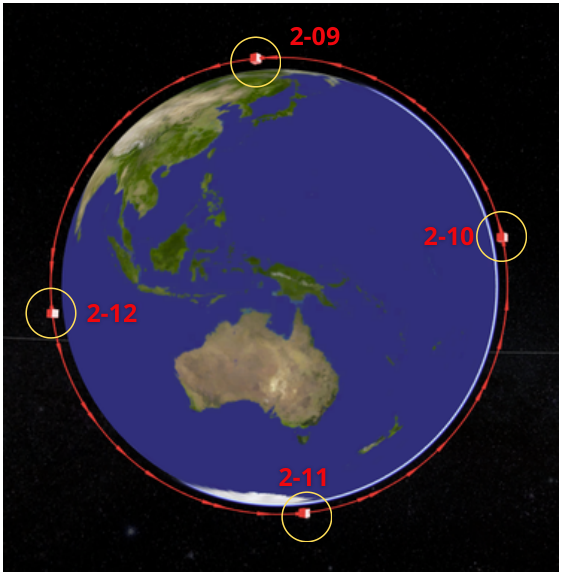
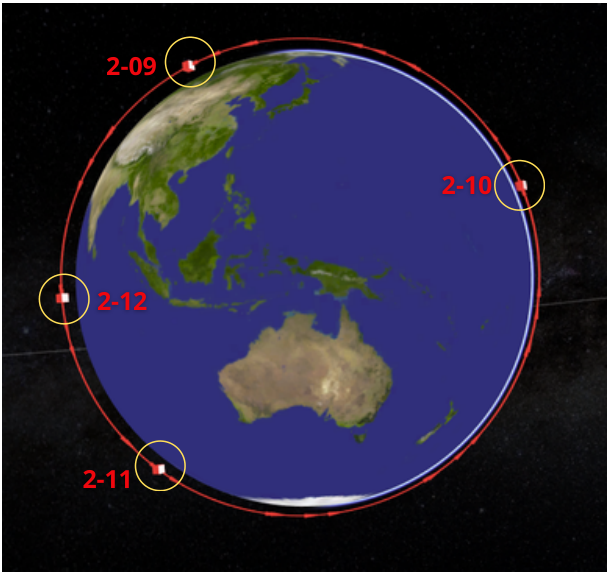
27 Dec 2025: PIESAT Group 3 In Distributed Formation with all 4 satellites separated by ~90° (left)
27 Sep 2026: PIESAT Group 3 No Longer Evenly Distributed due to slight SMA variations (right)
(saberastro.com)
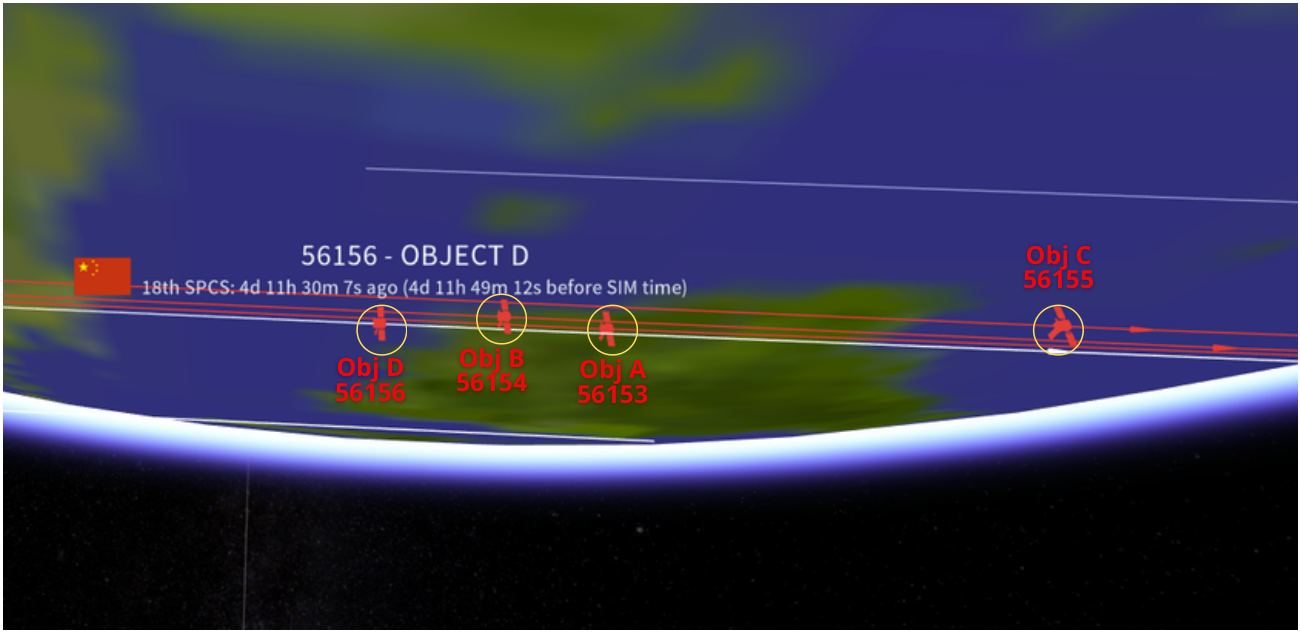
27 Sep 2026: PIESAT Group 1 Continues to Operate in Formation. Obj A appears to be the central node with Object B maintaining a consistent 4km, Obj C 12km and Obj D 6.5km separation from Obj A.
(saberastro.com)
China: 1st Qianfan Commercial Launches 15 Sep 2026: China conducted 2 commercial launches to support the deployment of the Qianfan (Thousand Sails) proliferated LEO constellation. First, a LandSpace ZhuQue-2E launched 10 SpaceSail satellite
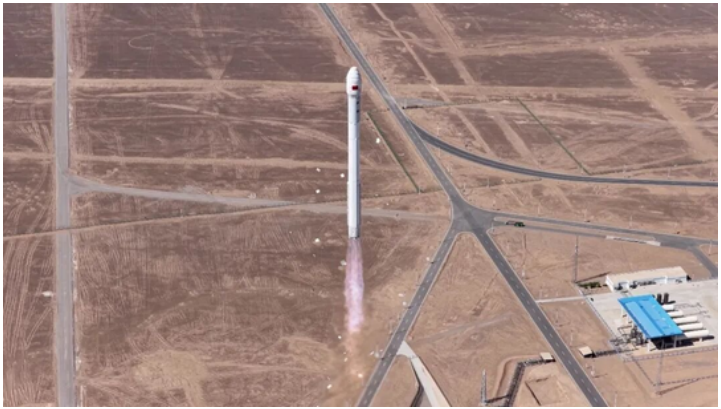
15 Sep 2026: China conducted 2 commercial launches to support the deployment of the Qianfan (Thousand Sails) proliferated LEO constellation. First, a LandSpace ZhuQue-2E launched 10 SpaceSail satellites (100692-100701) from the “Dongfeng Commercial Space Innovation Experimental Zone”, Jiuquan Satellite Launch Center. Chinese press releases labeled the satellites “Group 19.” Unclear if/when Groups 17 or 18 will be launched. China launched the satellites into the orbital plane with Group 1 & Group 12. Launch Video.
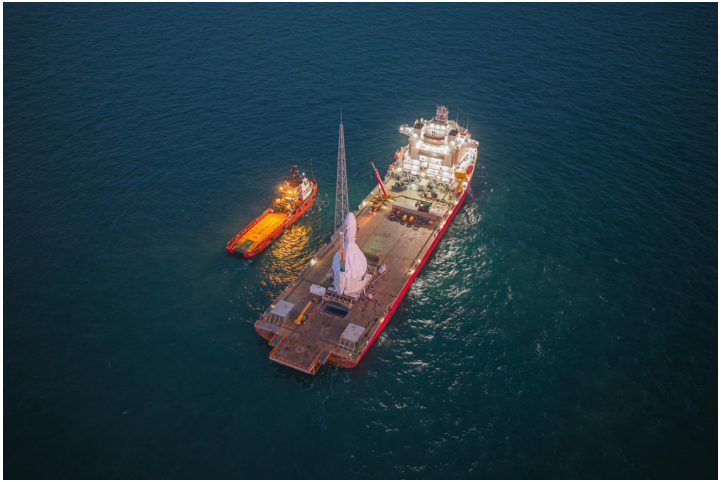
16 Sep 2026: Just 15.5 hours later China conducted a second Qianfan launch. This time a Gravity-1 launch vehicle launched 9 satellites, (1 EUHT technology test satellite (Ultra–high–speed wireless communication technology test satellite, 8 SpaceSail satellites (100702-100709), from a sea-based platform off the coast of Haiyang, Shandong Province. Chinese press releases labeled the satellites “Group 26.” Space-track.org has labeled the satellites as “Group 16”. China launched the satellites into the orbital plane with Group 3 & Group 10. Launch Video.
Two analytic notes: Groups 9–12 all reached operating SMA between 29 Jul and 4 Sep 2026, converting 74 satellites to operational in about five weeks. Quality issues seem to have been resolved as we haven’t seen a Qianfan satellite fail to reach its operational orbit since Group 6 which launched in October 2025.
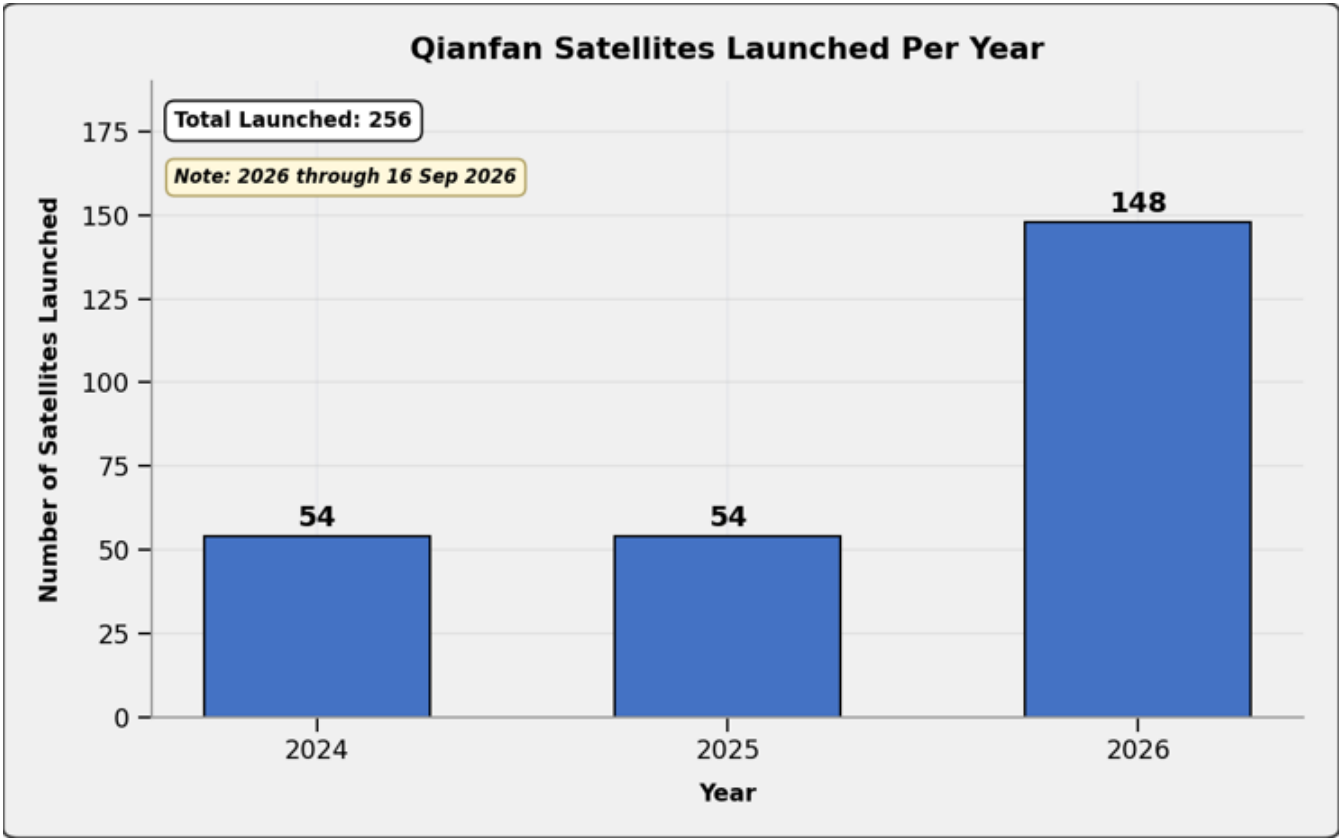
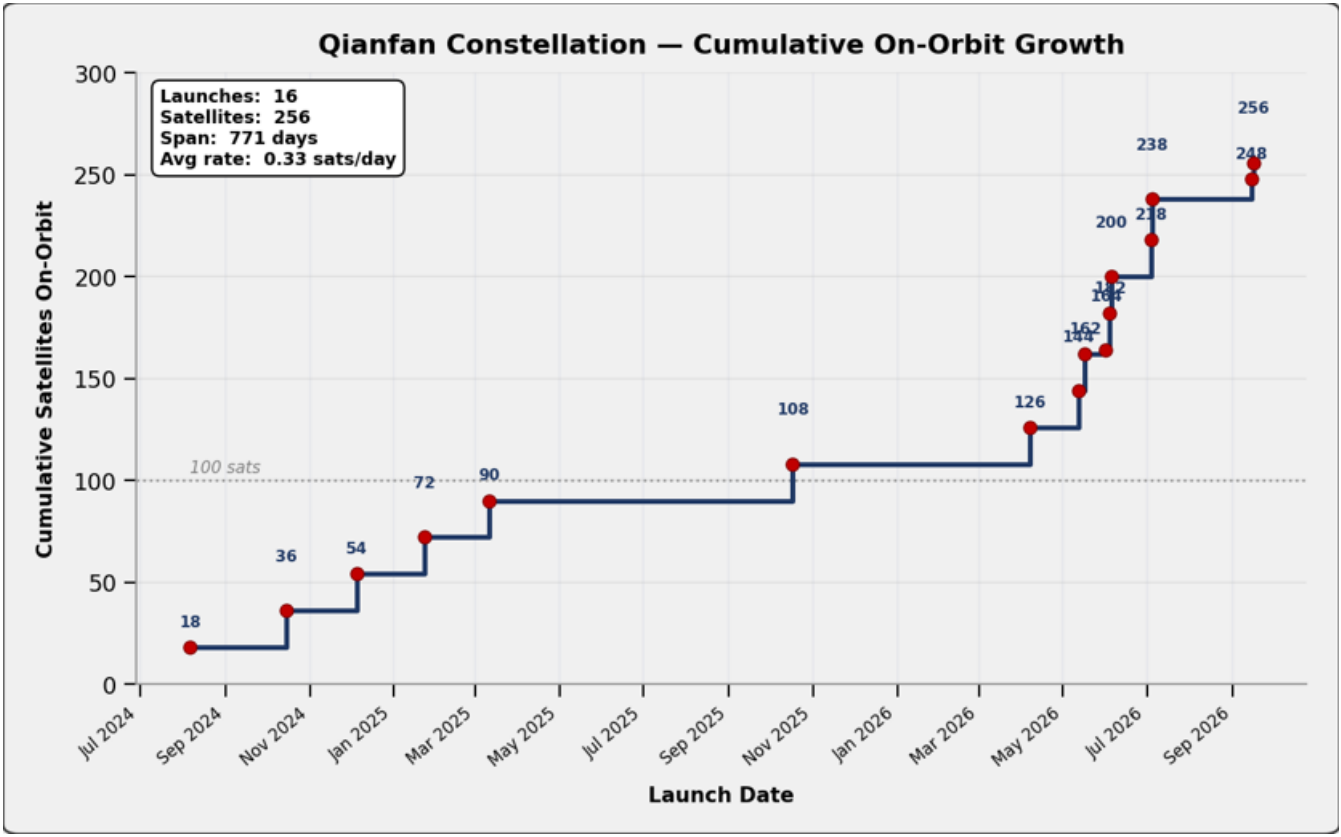
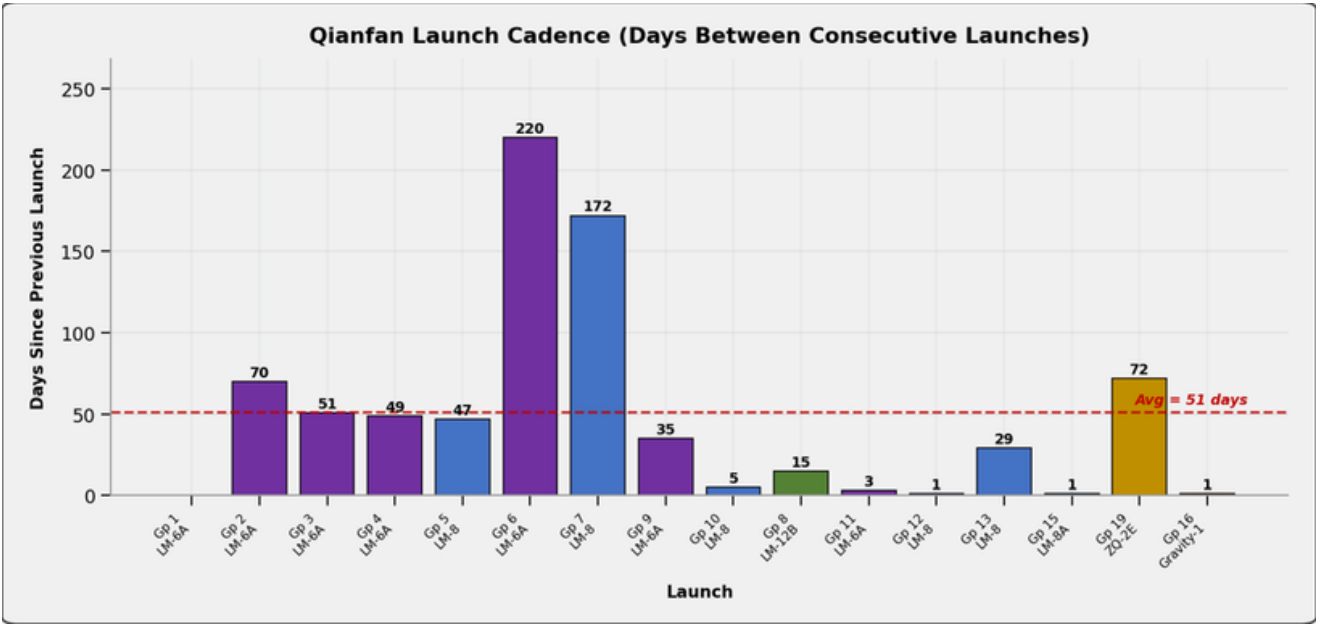
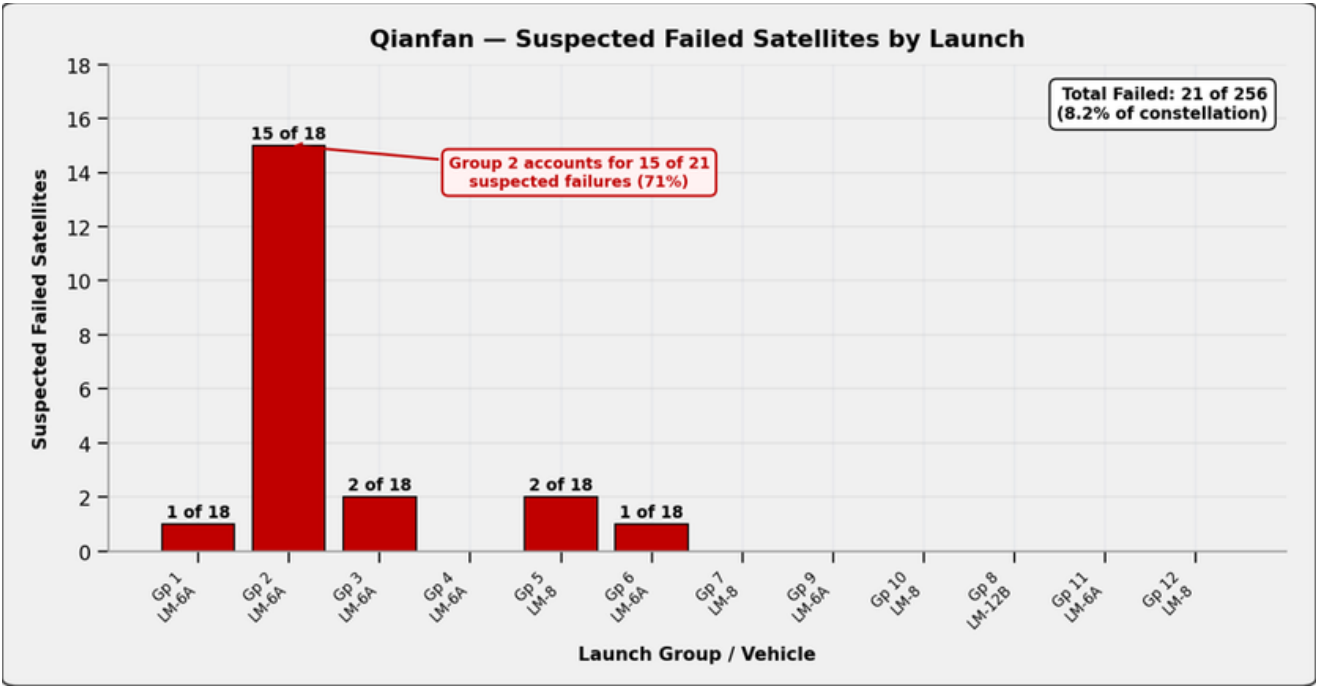
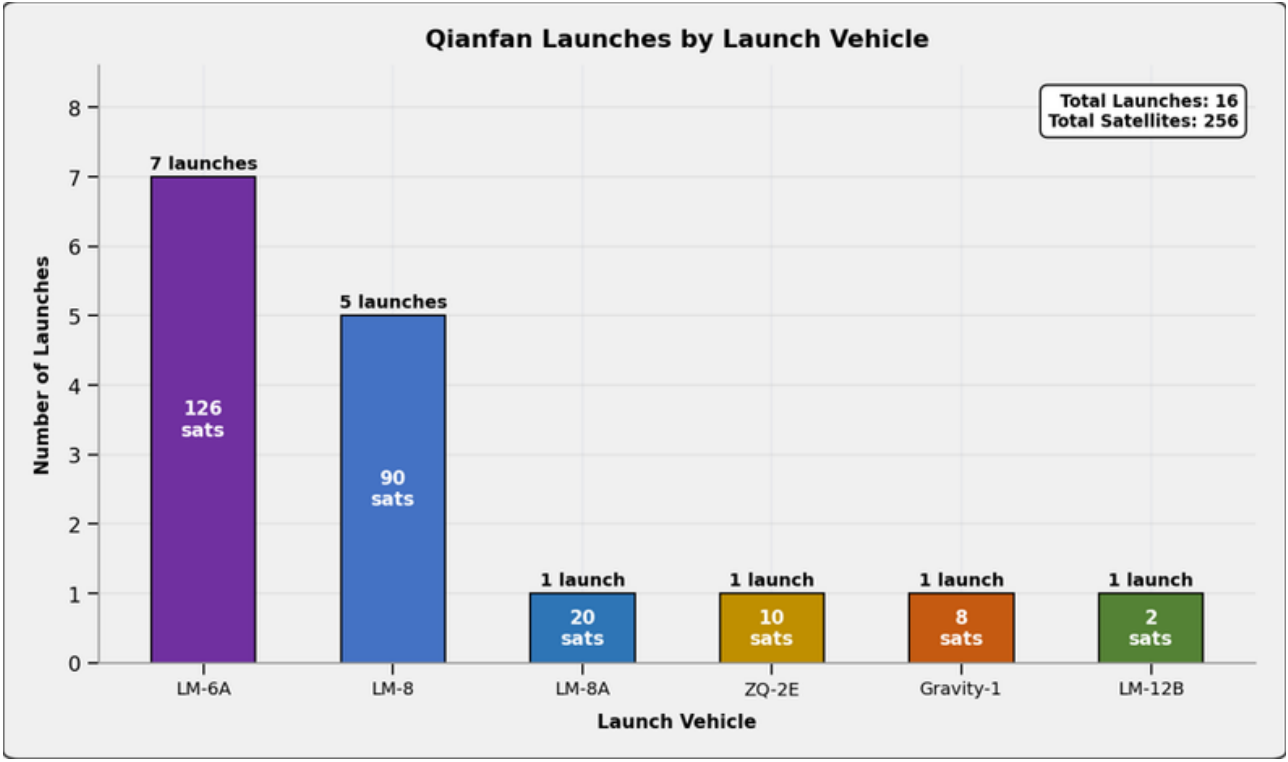
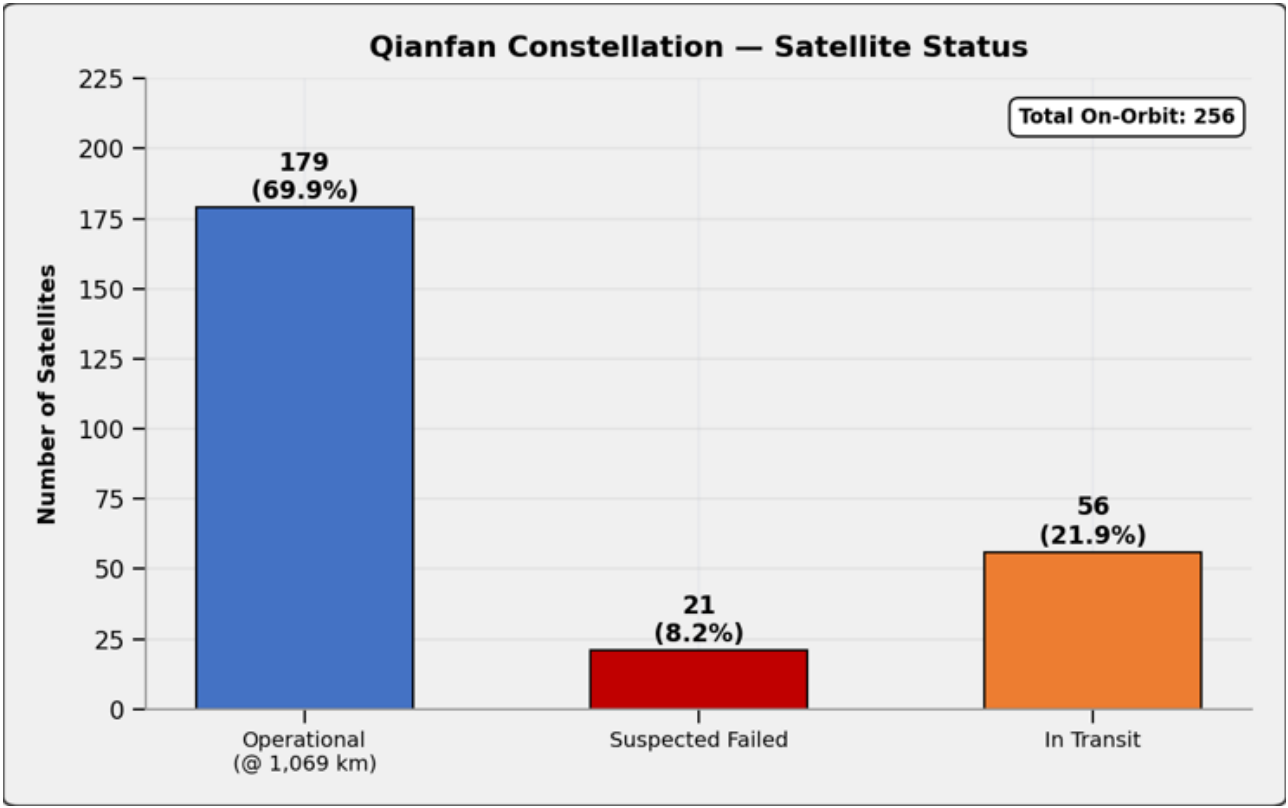
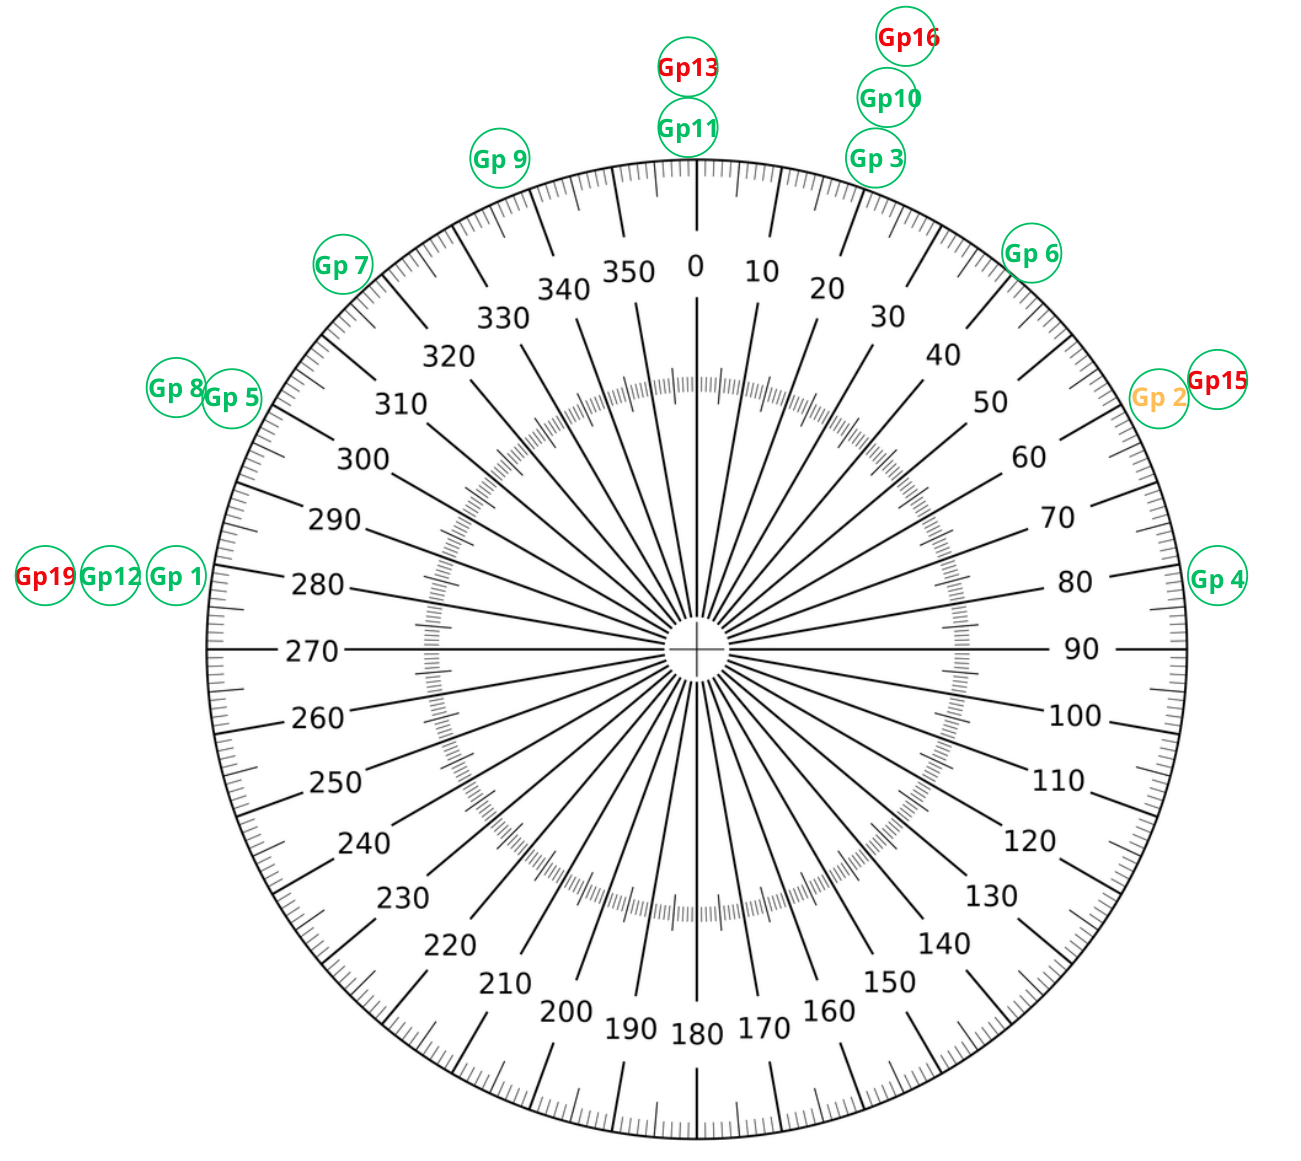
Current Qianfan Constellation consists of 256 satellites operating in 9 orbital planes. Planes are inclined 89° & separated by ~20° RAAN. (saberastro.com)
17 Sep 2026: China launched a Long March-12 with the 25th group of Guowang (China SatNet LEO) satellites from Wenchang. According to official sources, the 9 satellites (100714-100722) entered the preset orbit successfully. As with other Wen
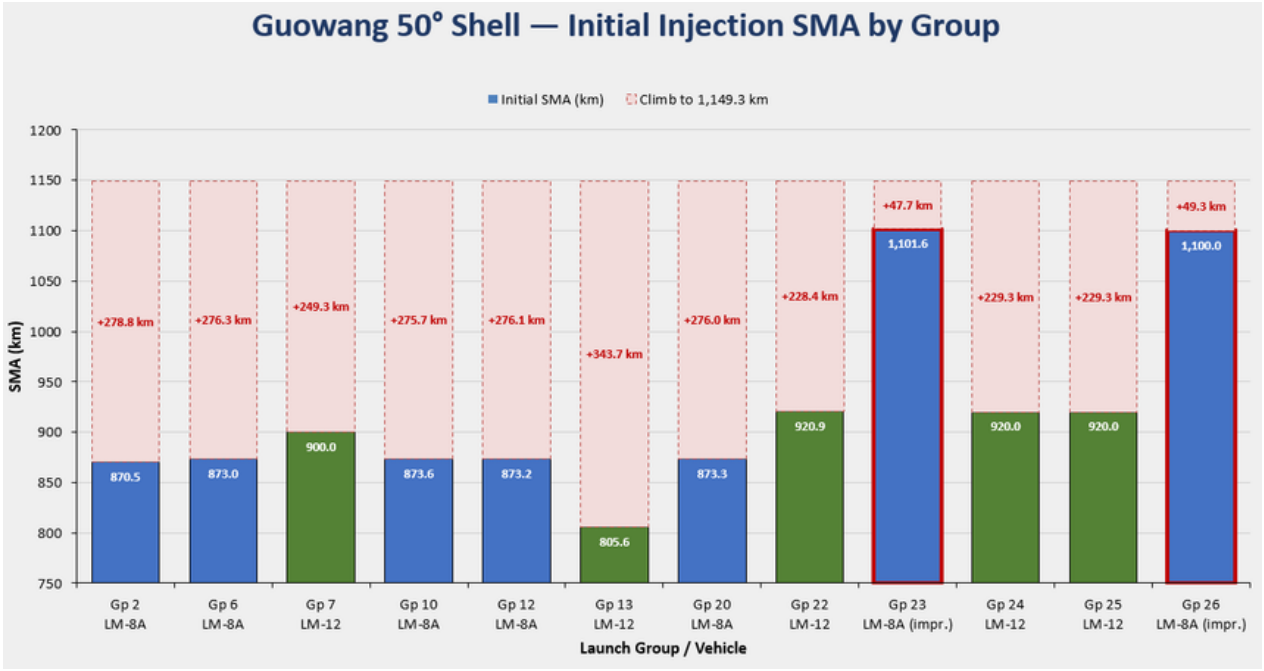
17 Sep 2026: China launched a Long March-12 with the 25th group of Guowang (China SatNet LEO) satellites from Wenchang. According to official sources, the 9 satellites (100714-100722) entered the preset orbit successfully. As with other Wenchang launches, China placed the satellites into an 50.0° inclined orbit. China launched Group 25 into an orbit only 14° east of Group 6. The LM-12 delivered its payload into 920km orbits, the satellites will slowly increase their altitudes to reach the desired 1,149km. Watch Group 25 Launch Video.
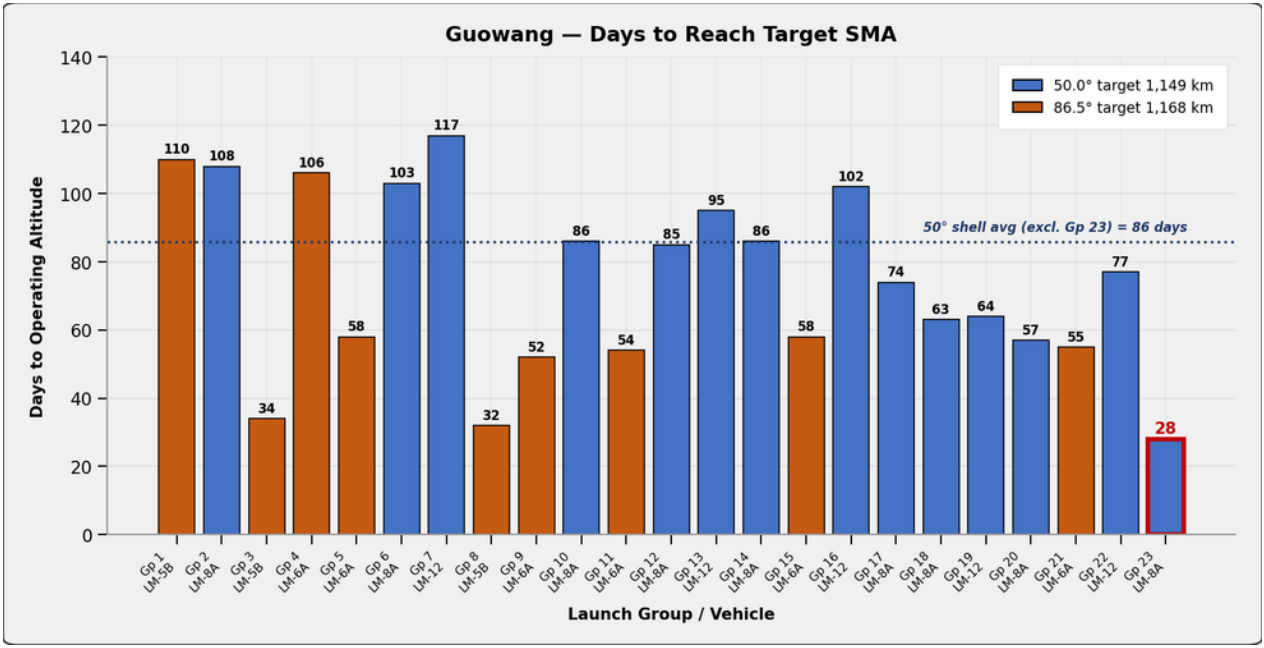
23 Sep 2026: China launched a Long March-8A with the 26th group of Guowang satellites from Wenchang. According to official sources, the launch carried 9 satellites (100791-100799) to their preset orbit successfully. As with the previous LM-8A launch, Group 26’s initial SMA was ~1,100km, versus the standard ~920km orbits from other launch vehicles. Using the LM-8A allows China to reach the operational orbit of 1,149km in only 28 days which is a 67% improvement from the average 86 days. Launching into a higher orbit allows China to place Group 26 closer to its intended operational plane. Group 26 has just a 0.4° east RAAN offset with Group 14. Launch Video.
DEPLOYMENT UPDATE: After ~77 days all 9 Group 22 satellites (launched 17 Jun 2026) reached their operational altitude of 1,149km and are now co-planar with Group 2. As noted above China used an improved LM-8A to launch its 9 Group 23 satellites into a significantly higher orbit >1,100km and as a result these satellites were able to reach their operating altitude in only 28 days. Group 23 satellites are co-planar with Group 10.
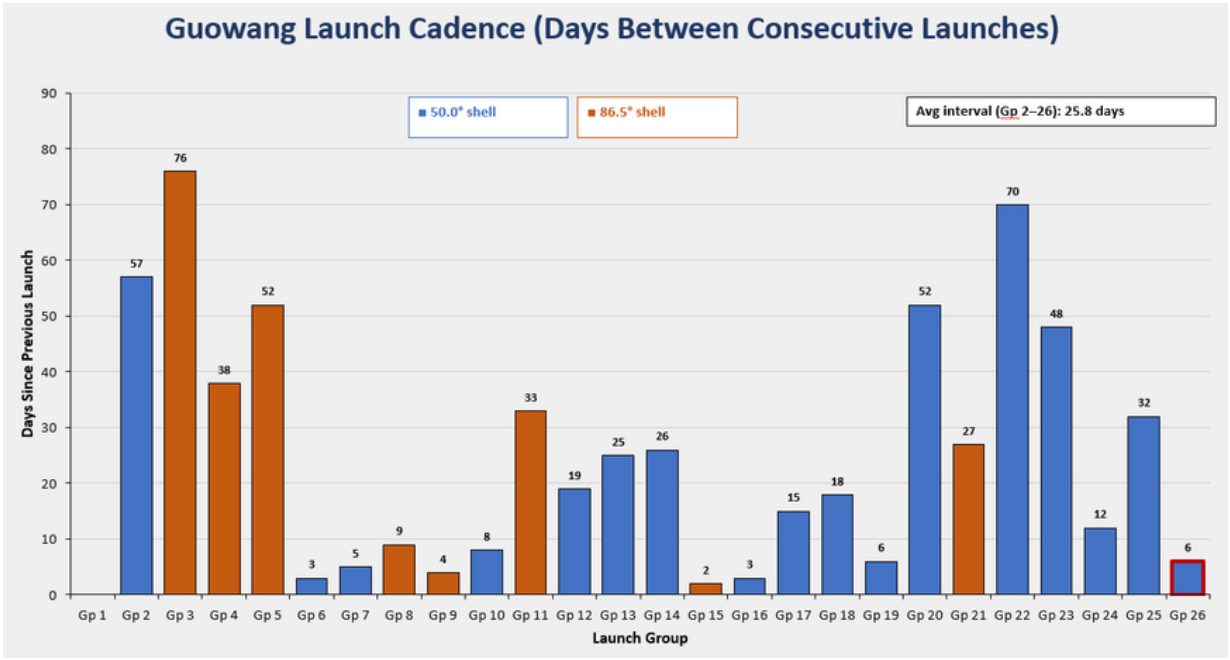
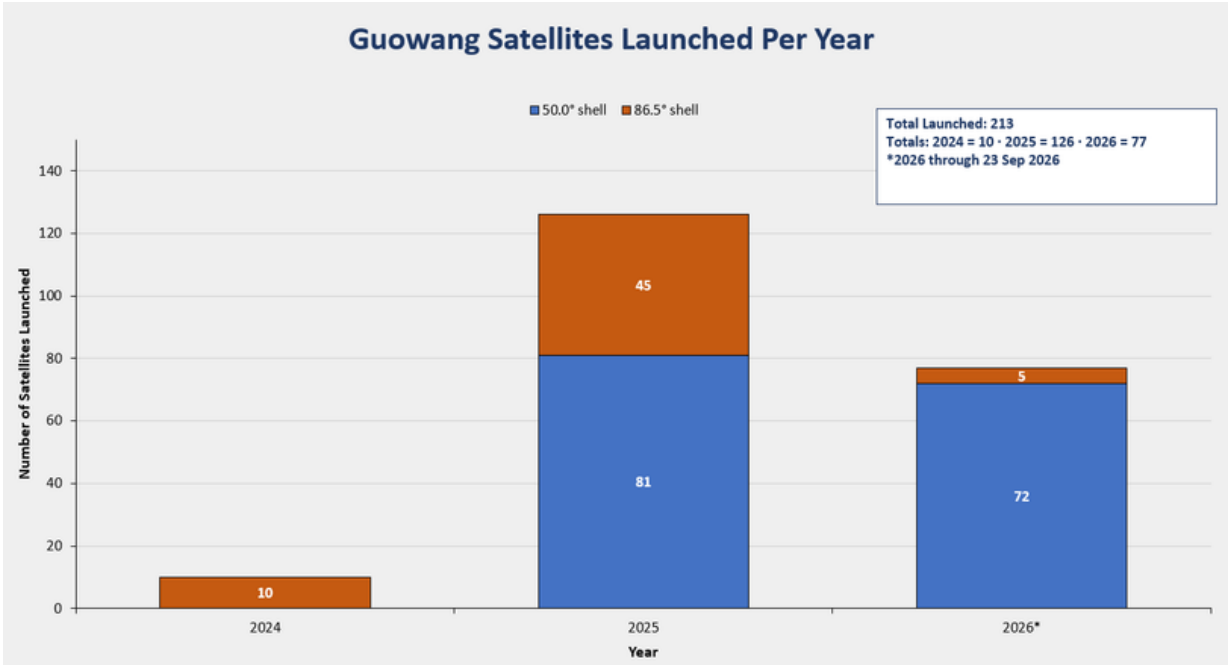
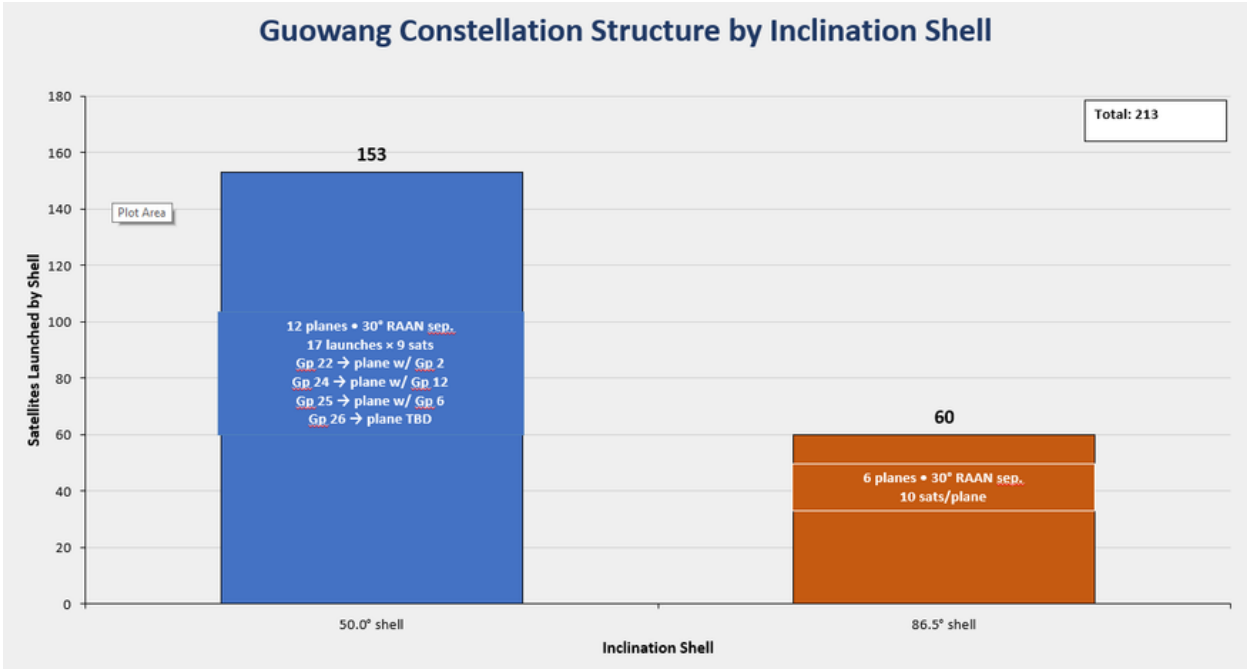
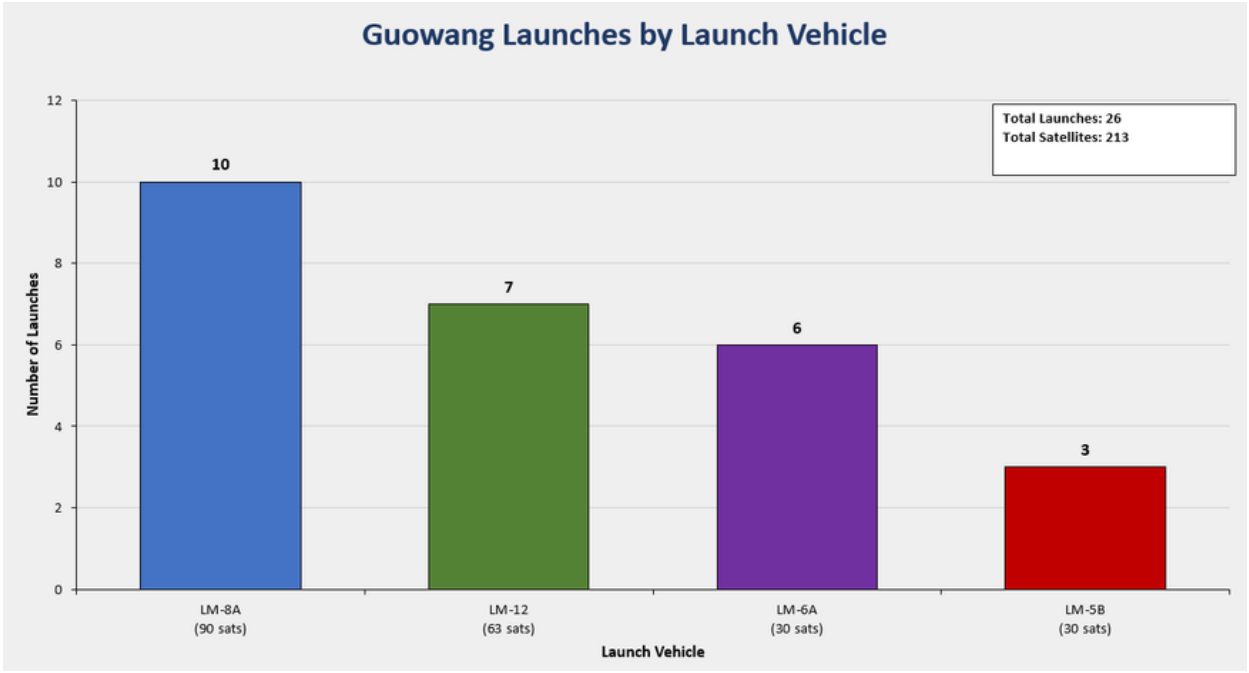
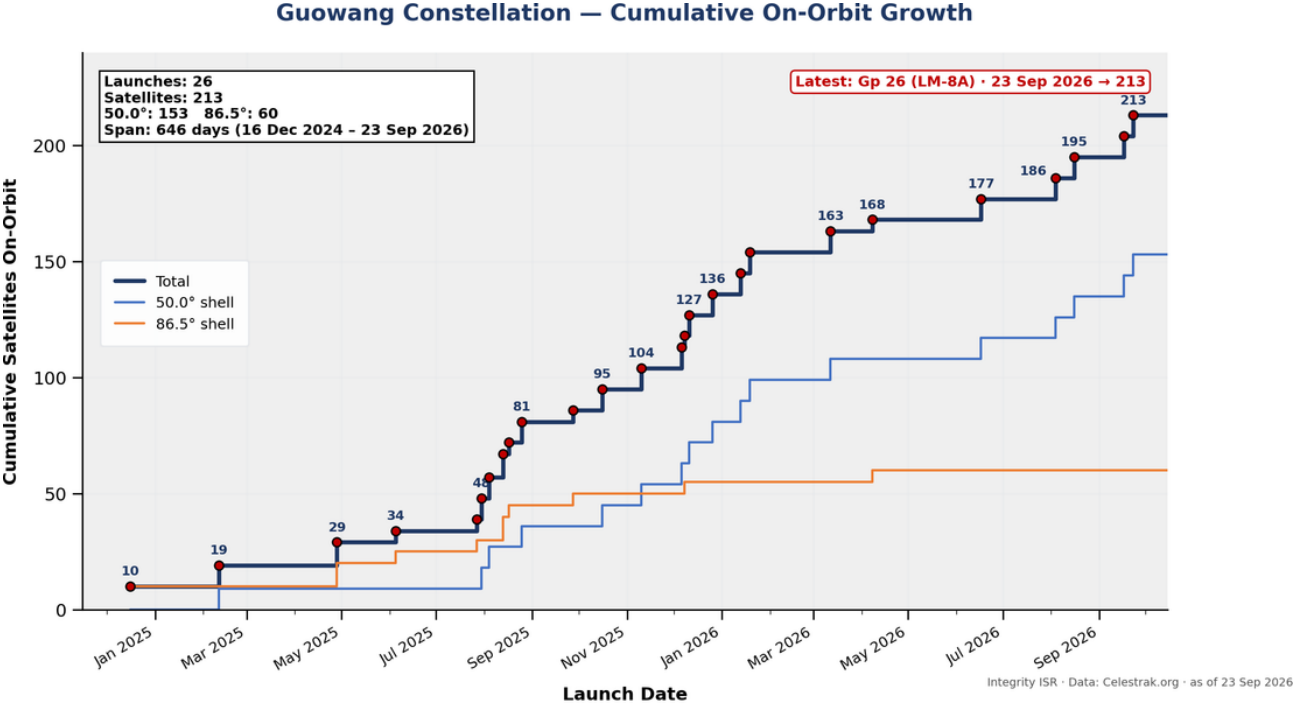
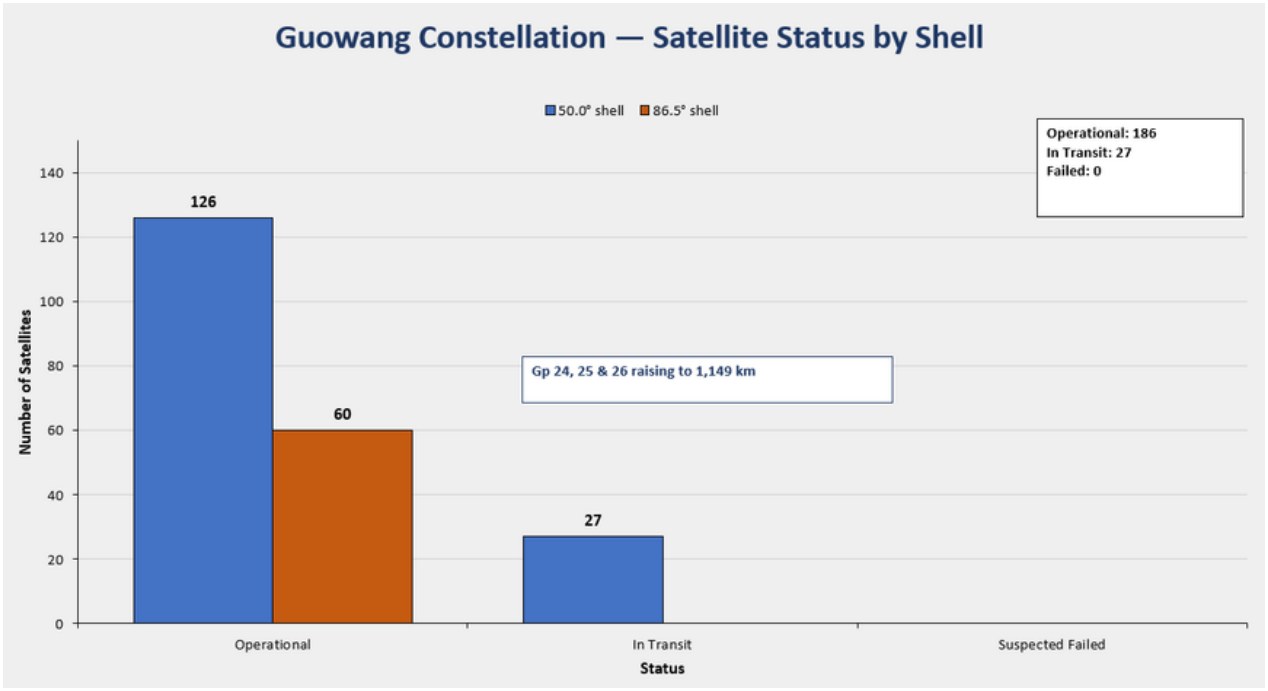
CONSTELLATION OVERVIEW: There are now 213 operational Guowang satellites in LEO (there are also 3 GEO satellites associated with Guowang). As of 23 Sep 2026, 23 of 26 Guowang groups have reached their operational altitudes. With a stated goal of reaching 310 satellites on orbit by 2027, China will need to launch 97 satellites in the next 3 months.
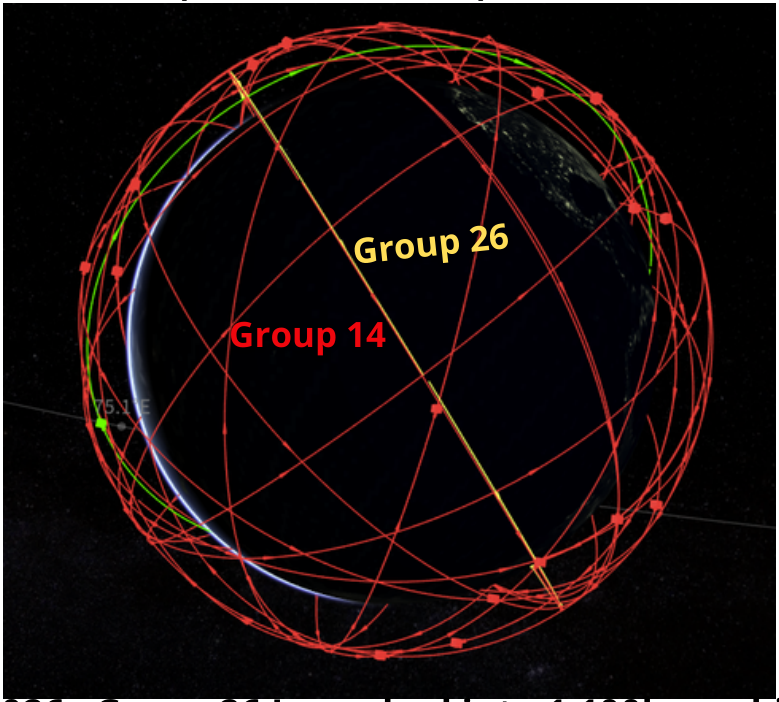
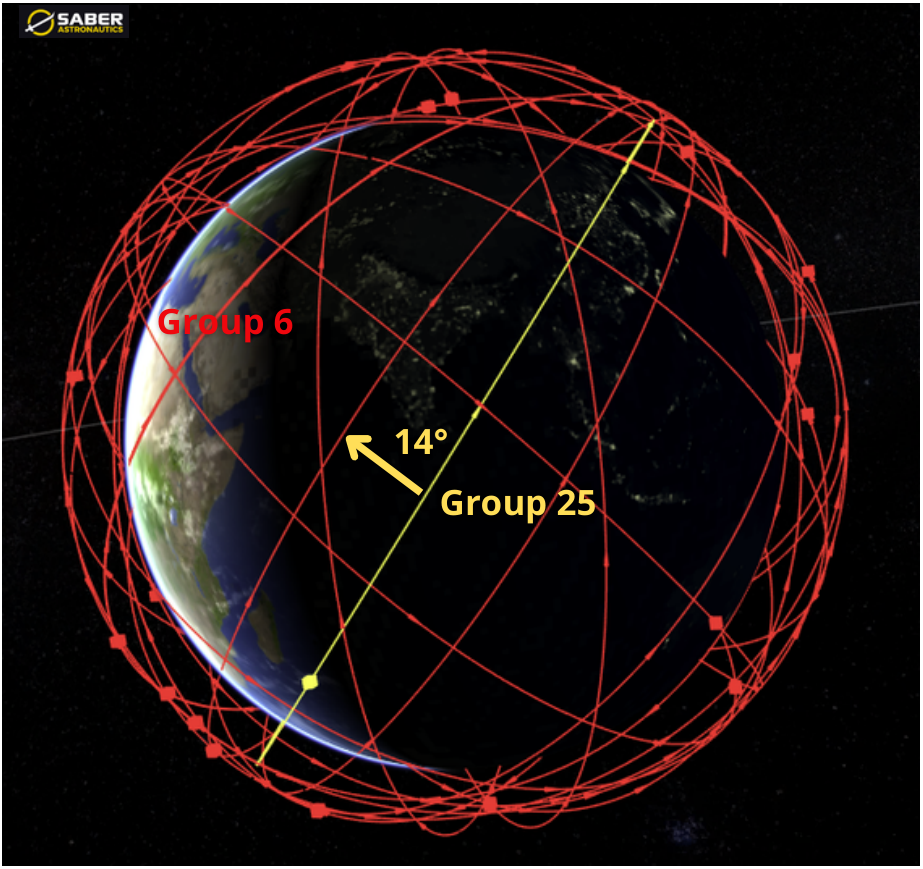
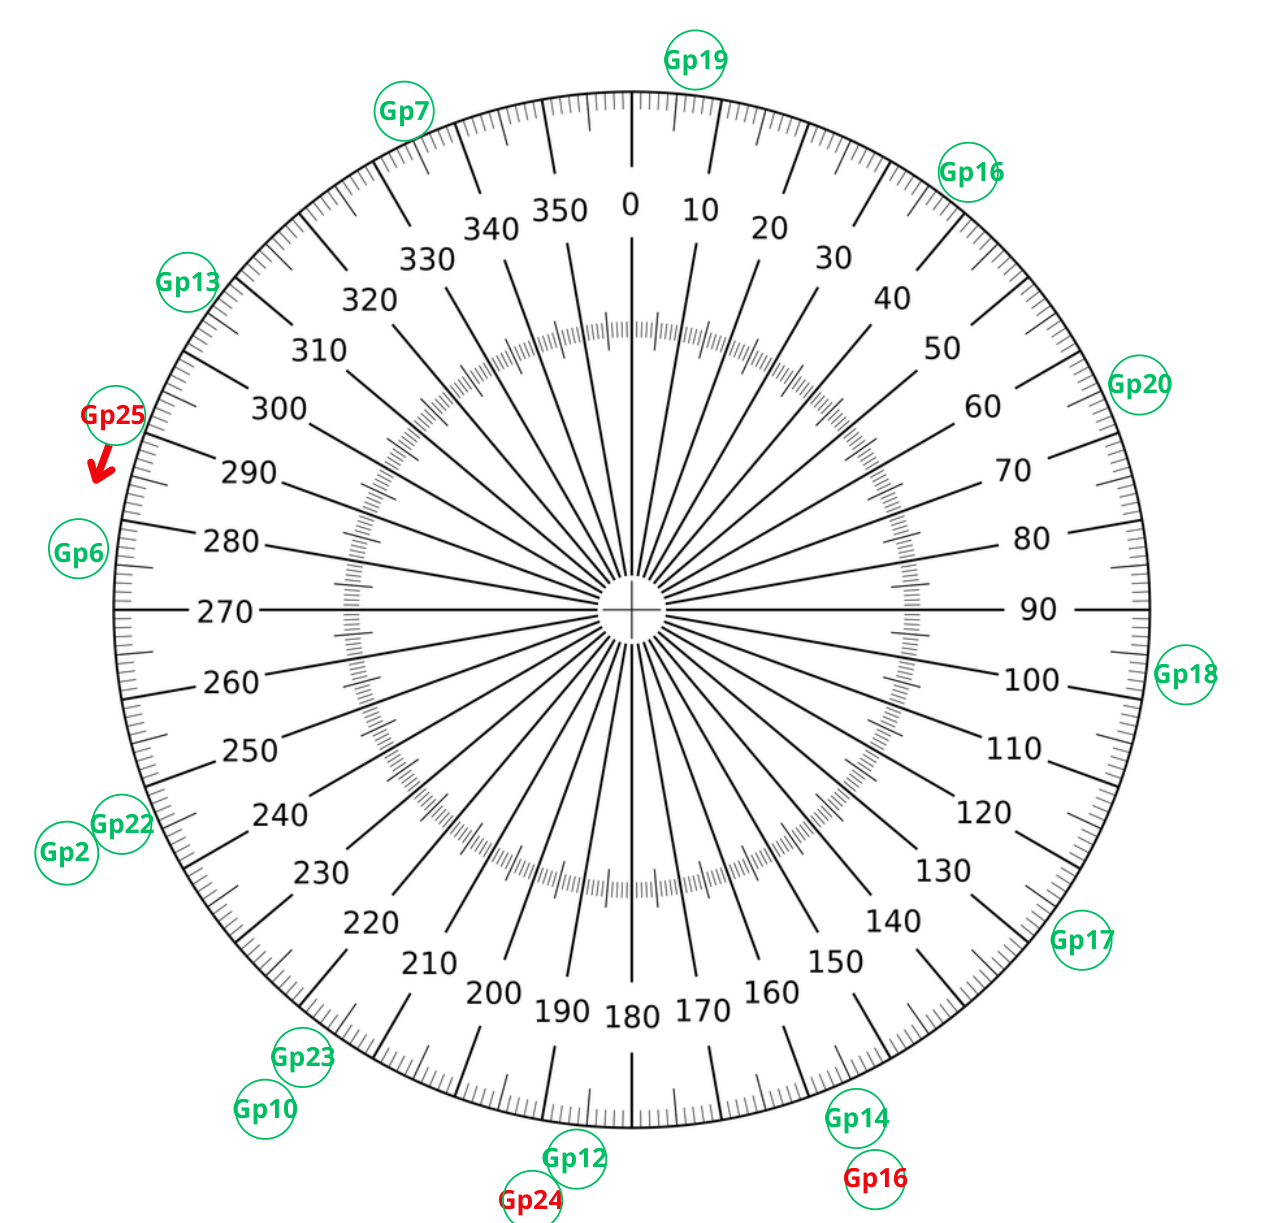
Constellation Overview Graphics: The Following Graphics are based on data from Celestrak.org.
Russia: Cosmos 2589 Update 25 Sep 2026: Russia's Cosmos 2589 (64467) continues to head east. Since 30 June, Cosmos 2589 has lowered its orbit twice, producing an eastward drift and carrying the satellite from its original GEO location of 98
25 Sep 2026: Russia’s Cosmos 2589 (64467) continues to head east. Since 30 June, Cosmos 2589 has lowered its orbit twice, producing an eastward drift and carrying the satellite from its original GEO location of 98.0°E to its current (as of 25 Sep 2026) 126°E.
Readers may recall that in the July edition of the Flash we reported Russia had reduced Cosmos 2589’s semi-major axis (SMA) by approximately 31 km between 20-24 July, initiating an eastward drift of roughly 0.4° per day. At the time the satellite had remained near 98°E for nearly three months following circularization and had been under close observation by both USA 325 and later USA 271.
Cosmos 2589 has been drifting eastward ever since. By mid-September the spacecraft had traveled roughly 20-25 degrees east of its original 98°E location. On 18 September, Russian operators initiated a second maneuver sequence which lasted 5 days and reduced Cosmos 2589’s SMA another 71km. At its new altitude (~94km below GEO) Cosmos 2589 drifted eastward ~1.1° per day. On 24–25 September Cosmos 2589 made two burns that raised its SMA and cut its eastward drift from 1.21 to 0.81°/day. Coincidentally (or not) these maneuvers occurred ~36 hours before a predicted close approach with USA 270 which has been near 126°E since ~8 Jul 2026. Per JCO reporting, by increasing Cosmos 2589’s SMA Russia increased its point of closest approach distance with USA 270 from 26.7–41.4 km to 112.3 km.
I’m not sure where (if?) Russia will increase Cosmos 2589’s SMA to reverse its eastward drift and head west. I do know Cosmos 2589 travelled as far east as ~144°E during its early months when it was in its highly elliptical geosynchronous orbit. If this is an operational boundary for Cosmos 2589 it will need to turn around in mid to late October depending on drift rate.
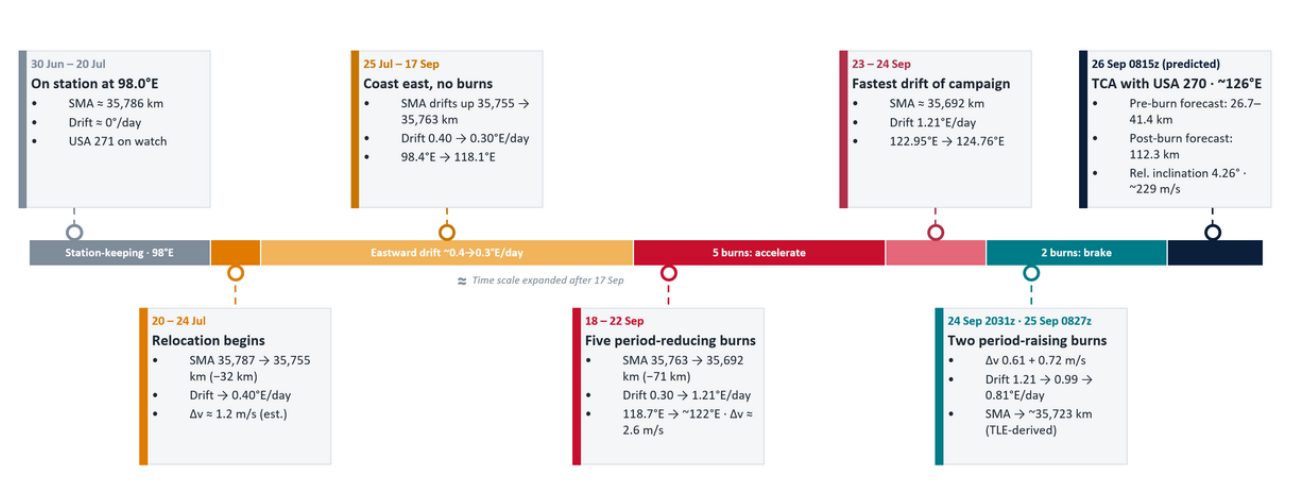
30 Jun-25 Sep: Cosmos 2589 Maneuvers and Drift Rates
(based on data from celestrak.org)
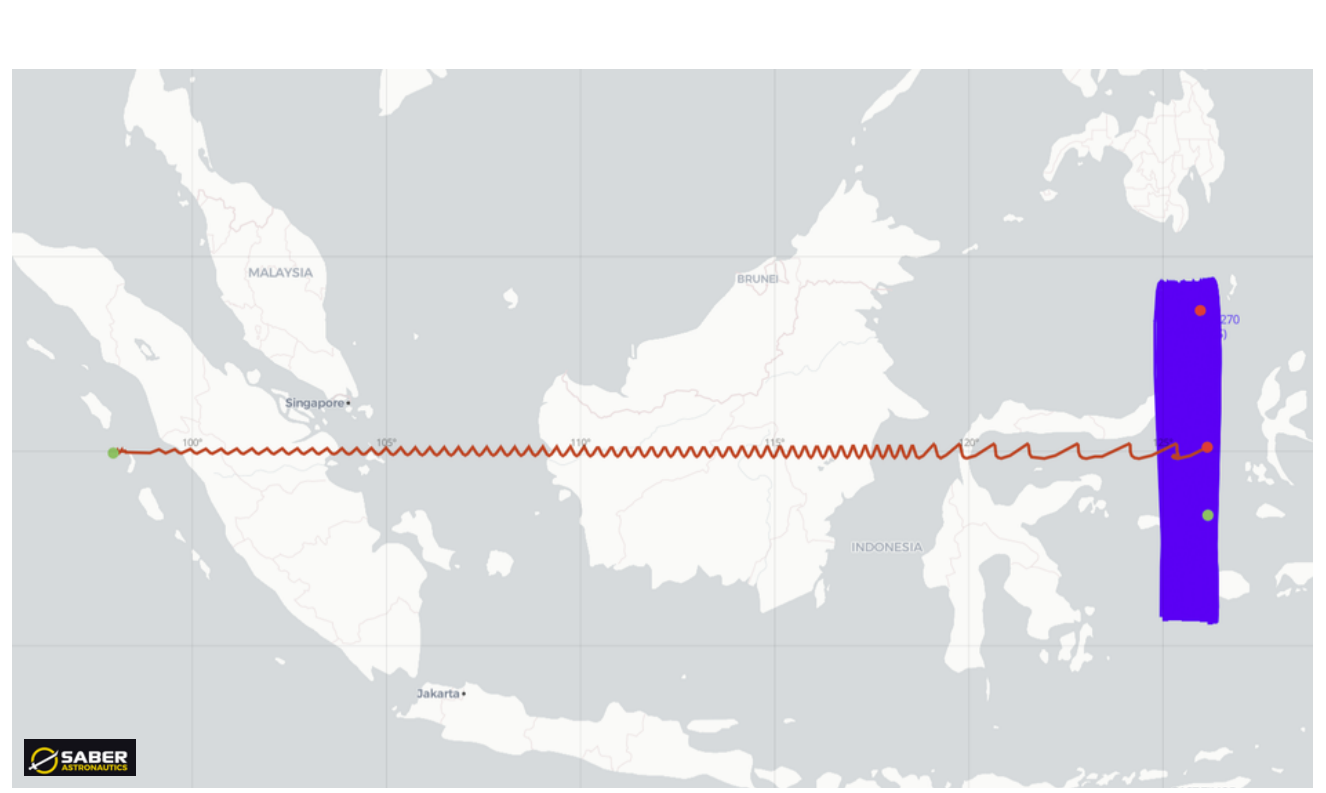
8 Jul-25 Sep 2026: Map View of Cosmos 2589 (red) eastward trek. Cosmos 2589 slowed its drift rate as it approached USA 270 (purple). (saberastro.com)
Editor’s Comment
Cosmos 2589’s mission remains unclear. Since arriving in GEO the satellite has demonstrated capabilities consistent with a potential inspection mission: deployment of a maneuverable subsatellite (Cosmos 2590), and unusual orbital maneuvering. The current relocation campaign raises several possibilities. Russia may simply be repositioning the satellite to a new operational longitude, surveying the GEO belt, or maneuvering towards a particular target of interest.
17 Sep 2026: Russia launched a Soyuz-2.1b/Fregat-M from Plesetsk carrying a GLONASS navigation satellite (100744). The payload is believed to be a GLONASS-K1 vehicle, reportedly No. 20L, and has been designated Cosmos 2620. Russian authorit
17 Sep 2026: Russia launched a Soyuz-2.1b/Fregat-M from Plesetsk carrying a GLONASS navigation satellite (100744). The payload is believed to be a GLONASS-K1 vehicle, reportedly No. 20L, and has been designated Cosmos 2620. Russian authorities made no immediate statement; Roskosmos acknowledged the mission the following morning with the now-standard boilerplate that the spacecraft reached its target orbit.
This is the second GLONASS replenishment launch in less than a month. As we reported in Integrity Flash Issue 153, Russia launched Cosmos 2619 (100460) on 24 August 2026 from the same pad, placing a GLONASS-K into a 64.77° inclined, 19,147 km orbit. Cosmos 2619 has yet to enter its operational slot and has increased its SMA to 19,161.3km and is now 46km above the nominal Plane 3 orbits. Prior to August, the last GLONASS-K launch had been in September 2025.
Over the past decade Russia has tended to launch 2 Glonass satellites/year (see graphic). It is worth noting that RussianSpaceWeb reported that the September launch window announcement “coincided with a number of reports about technical issues with in-orbit GLONASS satellites which could require urgent replacements”.
Launch security note: The NOTAM pattern again reflects Russia’s response to the Ukrainian drone threat against Plesetsk we covered in Issue 153. The September window ran 17–29 September, 11:00–23:59 Moscow Time. Russia announced a planned impact of rocket debris in Tyumen region 24 hours prior to the start of the launch window…an unusually short notice compared with previous Plesetsk launches, and possibly a deliberate new tactic to compress the predictable window during which a fueled rocket sits on the pad.
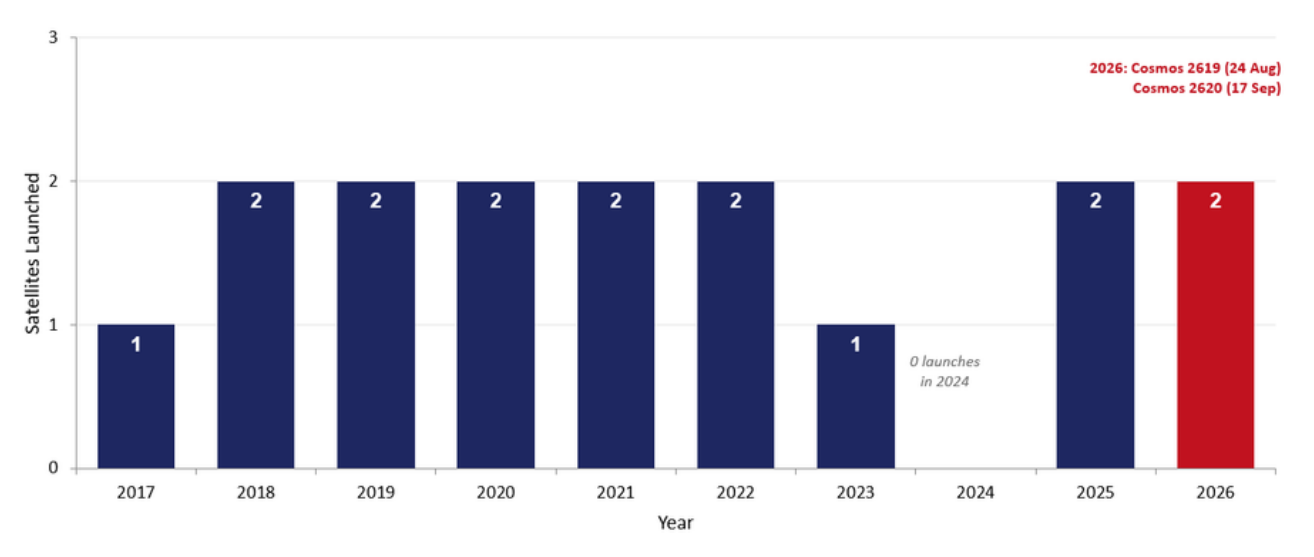
Glonass Launches 2017-2026
(RussianSpaceWeb.com; russianforces.org; Wikipedia List of GLONASS satellites)
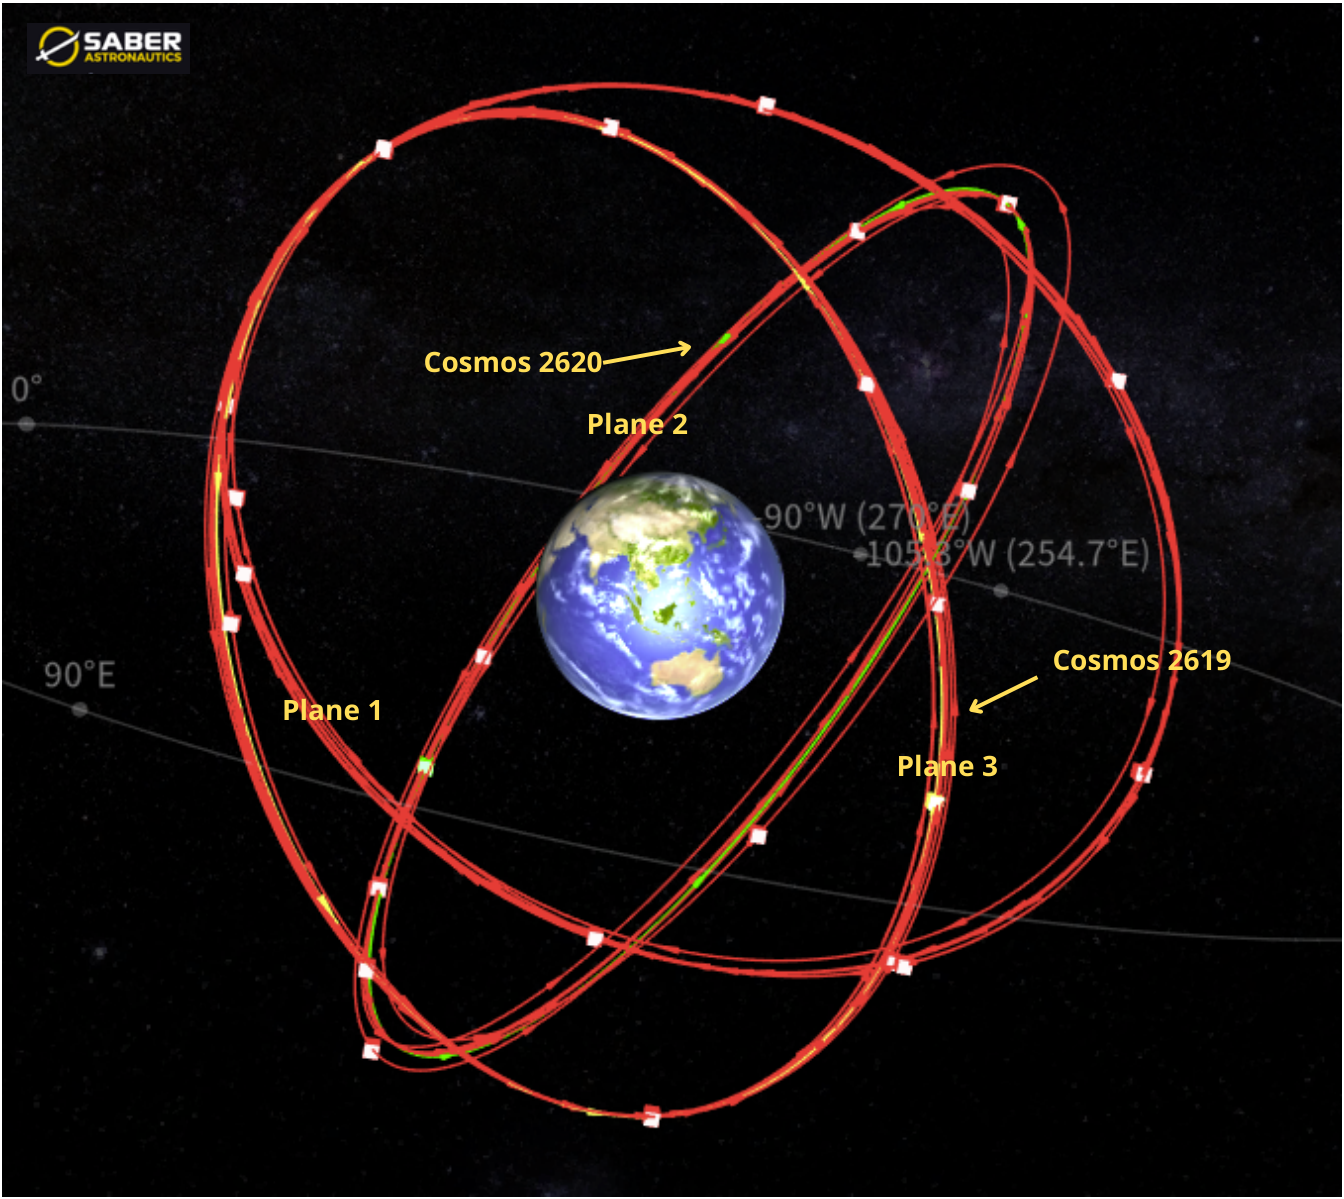
Cosmos Constellation: 3 Orbital Planes Inclined ~64.8° with 120° RAAN Offset
(saberastro.com)
by Alison Sayer 23 Sep 2026: A fire damaged a Starlink ground station in Wola Krobowska, roughly 50km south of Warsaw. The fire damaged electrical distribution equipment and a backup generator but did not knock the station offline. The faci
23 Sep 2026: A fire damaged a Starlink ground station in Wola Krobowska, roughly 50km south of Warsaw. The fire damaged electrical distribution equipment and a backup generator but did not knock the station offline. The facility is operated by Polish state-owned telecommunications company Exatel and supports Starlink connectivity in the region, including services used by Ukraine.
Polish Deputy Prime Minister and Digital Affairs Minister Krzysztof Gawkowski initially said the incident was being investigated as possible sabotage. By 25 September, Polish officials were more confident the fire had been deliberately set. Deputy Interior Minister Czesław Mroczek said available evidence, including CCTV footage, pointed to intentional arson. Polish security officials have raised the possibility of Russian involvement, but no perpetrator has been publicly identified and Poland has not formally attributed the attack to Russia.
Polish officials have also framed the incident within the broader context of Russian hybrid warfare against Europe. Gawkowski said the fire appeared consistent with a new phase of hybrid activity targeting critical infrastructure, while other Polish officials pointed to a wider pattern of sabotage, arson, cyber activity, and disruption linked to Russian intelligence operations. At the same time, Poland has not publicly attributed the Starlink fire to Russia, and investigators have not identified a perpetrator.
That framing matters because the station supported Starlink connectivity used by Ukraine. If the fire was intended to disrupt that support, it would fit an established pattern of pressure against European infrastructure enabling Ukraine’s war effort, but through methods that remain below the threshold of direct military attack and can complicate attribution and response.
If the sabotage assessment holds, the Starlink station fire is less notable as a technical attack on satellite communications than as another example of space support infrastructure becoming part of a broader hybrid campaign. The target was terrestrial, the effects were limited, and attribution remains unresolved, but the incident sits at the intersection of commercial space infrastructure, European critical infrastructure protection, and continued Russian pressure on states supporting Ukraine.
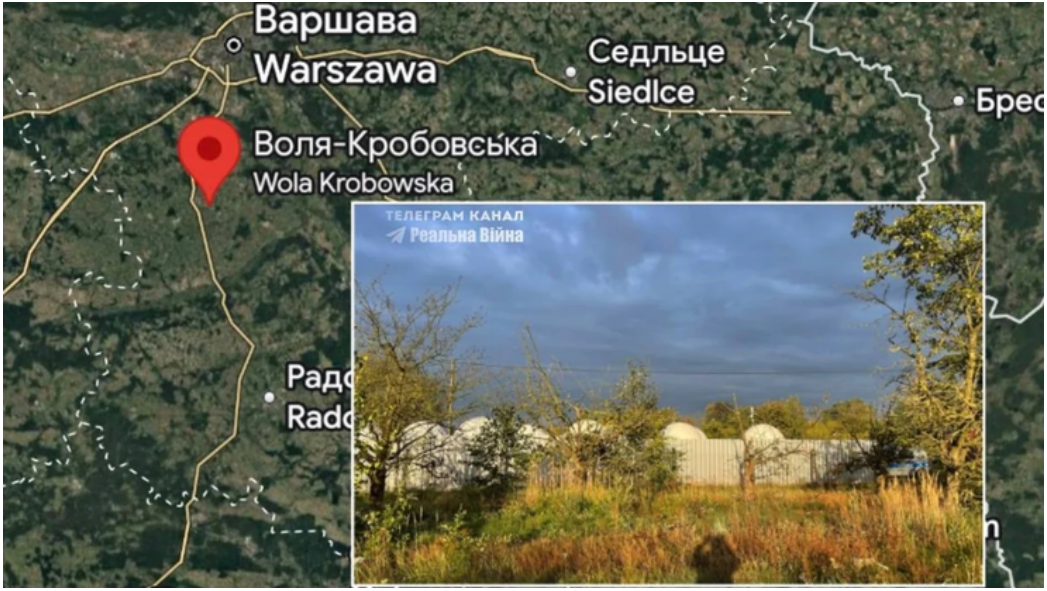
Map & Image of Damaged Starlink Groundsation in Poland
(https://ukrmedia.news/)
By Dr. Larissa Beavers For those just joining us please see Part 1 . A satellite may ultimately operate hundreds or thousands of kilometers above Earth, but its cybersecurity story begins much closer to home. Before reaching orbit, a spacec
For those just joining us please see Part 1.
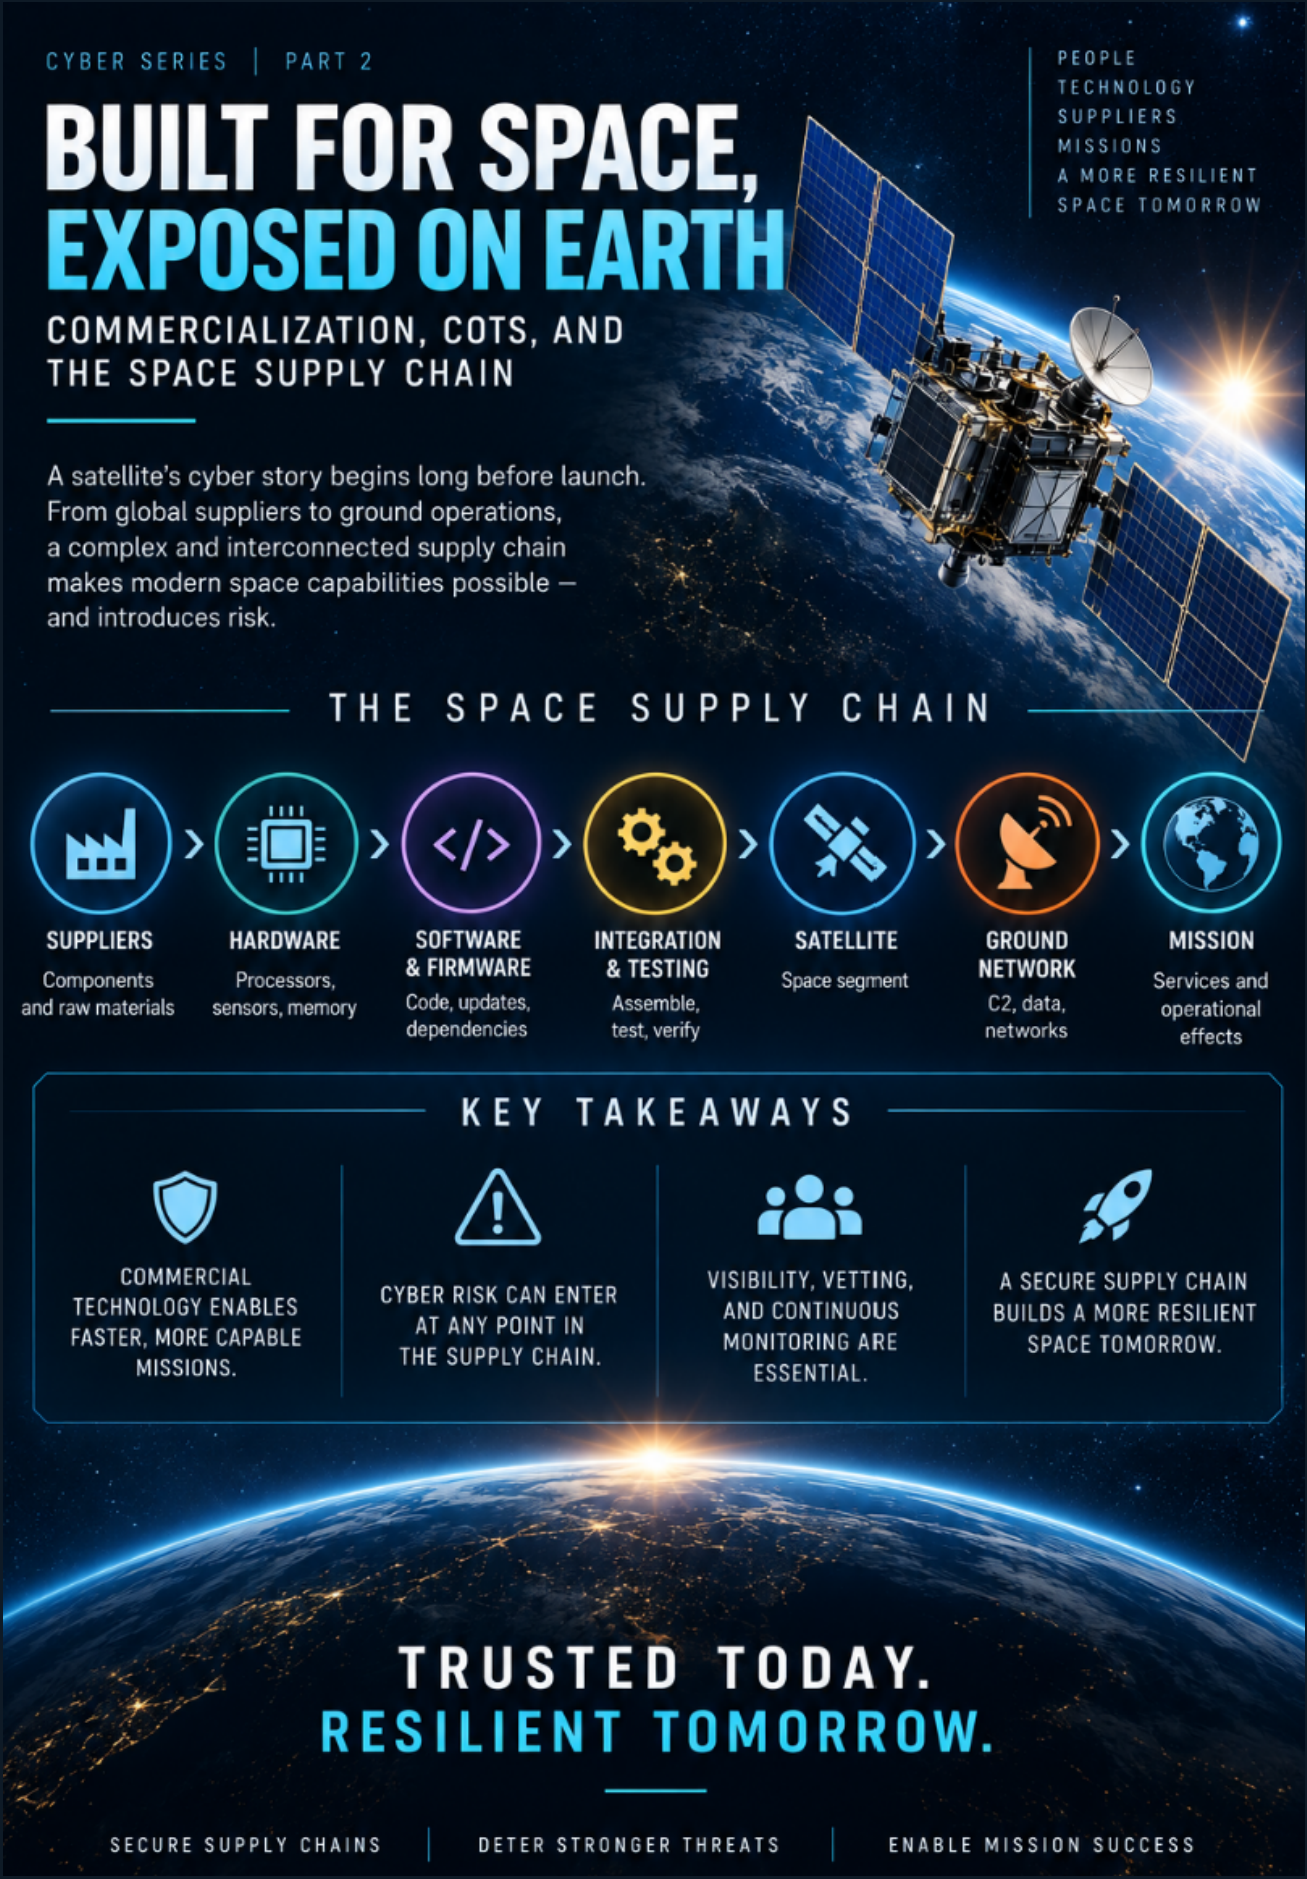
A satellite may ultimately operate hundreds or thousands of kilometers above Earth, but its cybersecurity story begins much closer to home. Before reaching orbit, a spacecraft passes through an extensive ecosystem of manufacturers, suppliers, software developers, integrators, test facilities, launch providers, and network operators. Its processors, memory, sensors, communications equipment, firmware, operating systems, and software may originate from different companies and locations around the world. Increasingly, some of those technologies were not originally designed exclusively for space.
Commercialization has transformed the space industry. Technologies that once required expensive, purpose-built development can increasingly be purchased, adapted, integrated, and launched on much shorter timelines. The U.S. Space Force has embraced that change; Space Systems Command wrote in June 2026 that commercial and dual-use technologies have become essential to maintaining U.S. space capabilities as technology and threats evolve rapidly.
But speed and accessibility introduce a cybersecurity question that extends beyond the satellite itself:
How well do we understand—and trust—everything we put inside it?
From Custom Built to Commercially Available
Historically, many government spacecraft relied heavily on specialized components developed for specific missions and the demanding environment of space. That approach offered substantial control over design and testing, but it was also expensive and slow.
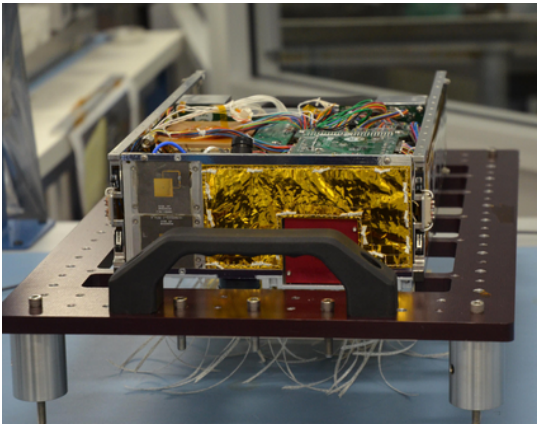
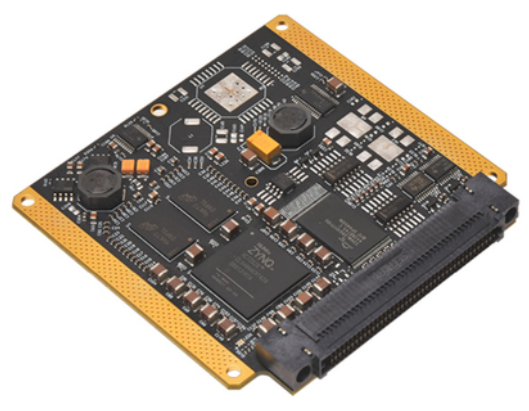
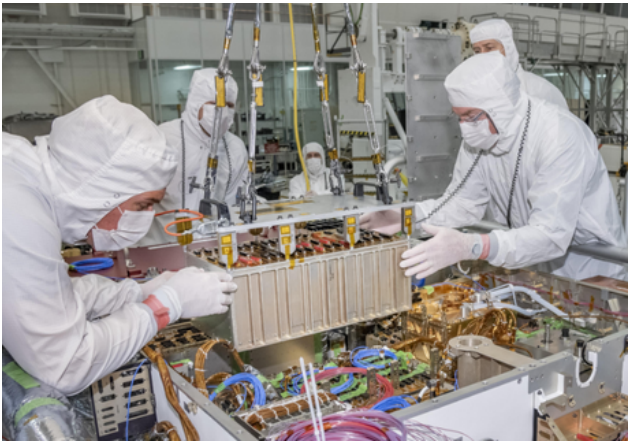
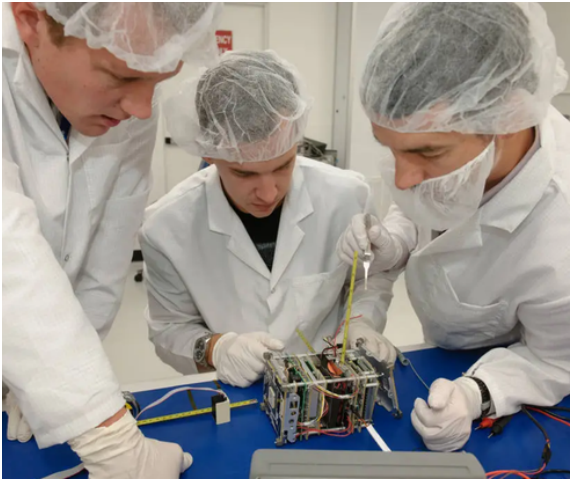
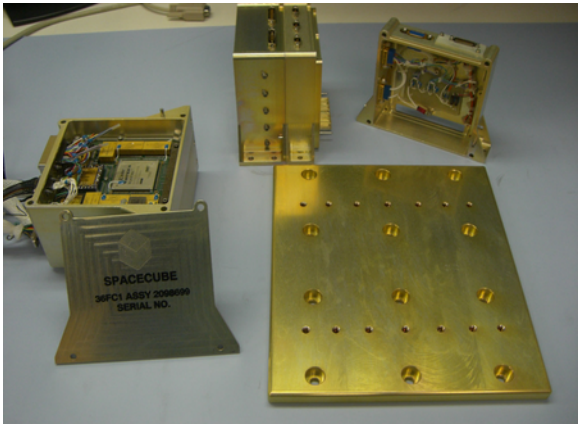
Commercial off-the-shelf, or COTS, technologies offer another option. COTS components, Figure 1 and 2, are commercially available products that can be purchased rather than developed specifically for an individual mission. NASA has used commercial hardware because it can reduce development and certification time, and the agency continues to evaluate COTS electrical, electronic, and electromechanical components for space applications.
The benefits are significant. Commercial technologies can reduce cost, shorten development schedules, provide access to rapidly improving computing capabilities, and allow smaller organizations to develop increasingly sophisticated spacecraft.
The tradeoff is that the spacecraft developer may no longer control—or even have complete visibility into—every layer of the technology being incorporated. A processor can contain intellectual property developed elsewhere. Software may rely on open-source libraries. Firmware may originate with a supplier. Hardware may pass through distributors and subcontractors before reaching the spacecraft integrator. The spacecraft may be assembled in one clean room, but its digital ancestry can span the globe.
The Supply Chain Becomes Part of the Attack Surface
This is where the issue shifts from acquisition to cybersecurity. NASA defines Information and Communications Technology Supply Chain Risk Management as identifying, assessing, and mitigating risks associated with the distributed and interconnected nature of technology supply chains. NASA specifically applies those assessments to COTS hardware, software, and cloud services and identifies security, integrity, and resilience of mission-critical systems and components as objectives. The concern is not simply where a component was manufactured. Cyber supply-chain risk can exist throughout a product’s lifecycle:
Design → Software → Components → Manufacturing → Integration → Testing → Updates → Operations
A vulnerability could be unintentionally introduced through poorly secured software. A compromised development environment could affect code before delivery. Counterfeit hardware could enter through an untrusted supplier. Firmware could contain an exploitable vulnerability. An open-source dependency could later be discovered to have a security flaw.
More deliberately, a sophisticated adversary could attempt to compromise a supplier or development environment (Figures 3 and 4) rather than attacking the finished spacecraft directly. That distinction matters. The satellite manufacturer does not have to be compromised if an attacker can compromise something the manufacturer trusts.
NASA highlighted this broader problem in April 2026. The agency noted its increasing reliance on COTS, open-source, vendor-supplied, and partner-developed software increases exposure to supply-chain issues and cited major terrestrial incidents such as SolarWinds and XZ Utils as examples of how weaknesses in software understanding can create systemic risk. Those incidents did not involve satellites. Their relevance to space is the attack model: compromising a trusted component or supplier can provide access farther downstream.
Software May Be the Component You Cannot See
A spacecraft component does not need to contain malicious hardware to introduce cyber risk.
Modern satellites depend heavily on software. Flight software processes commands. Firmware controls hardware. Operating systems manage computing resources. Communications software moves information between components. Ground software allows operators to monitor and control spacecraft. That creates an important challenge: A spacecraft can be physically inspected without revealing everything its software will eventually do.
NASA’s current software engineering requirements explicitly require cybersecurity assessments to account for risks associated with COTS, government off-the-shelf, modified off-the-shelf, open-source, and reused software components (Figure 5). The objective is to identify vulnerabilities capable of affecting mission confidentiality, integrity, or availability.
This is where commercial technology creates both opportunity and complexity.
NASA’s newer High-Performance Spaceflight Computing architecture (Figure 6) illustrates how capable these systems are becoming. Modern spaceflight processors can support high-speed networking, autonomous processing, multiple sensors, continuous system-health monitoring, and integrated security functions.
More capability, however, means more software—and potentially more code, dependencies, interfaces, and update mechanisms that must be understood and protected.
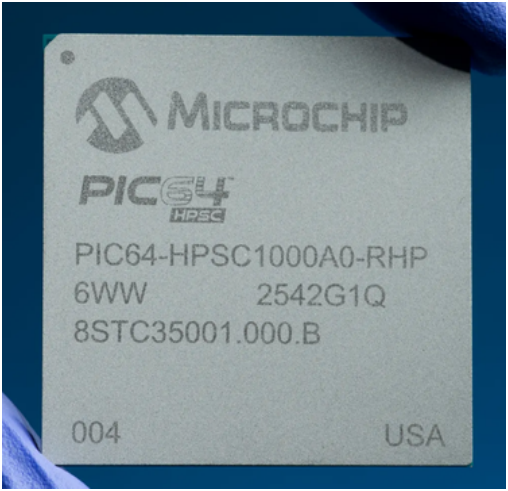
Figure 6: High Performance Spaceflight Computing System Chip NASA
Trust, but Verify
None of this means commercial technology should be avoided. In fact, that would miss the point. The U.S. government increasingly considers commercial space capabilities essential. A GAO report released in August 2026 notes that DoD already relies on commercial companies for space-derived data and services supporting national security. The challenge is therefore not: COTS or no COTS? It is: How do we use commercial technology while understanding and managing the cyber risk we inherit with it? NASA’s approach to COTS electronics illustrates this distinction. The agency maintains guidance for “Established COTS Parts” from manufacturers that provide sufficient product and company information to support evaluation. Even then, NASA notes that individual programs must determine whether components meet their particular mission, environment, application, and lifetime requirements.
Cybersecurity Cannot Begin at Launch
Space Policy Directive-5 specifically identifies supply-chain management as a component of space-system cybersecurity. It calls for tracking manufactured products, using trusted suppliers, identifying counterfeit, fraudulent, and malicious equipment, and evaluating available risk mitigations. That is an important shift in thinking:
Supply-chain security is not separate from spacecraft cybersecurity. It is one of its earliest layers.
A compromised laptop can be removed from a network. A server can be replaced. Technicians can physically access terrestrial infrastructure.
Most satellites do not offer that luxury.
Space Policy Directive-5 therefore emphasizes that cybersecurity needs to be integrated into spacecraft design before launch, including the capability to update systems and respond to cyber incidents remotely. It calls for cybersecurity throughout the entire space-system lifecycle rather than treating security as something added after development.
Spacecraft integration may occur in a tightly controlled clean room (such as Figure 7), but the hardware and software being assembled can originate from a much broader supplier ecosystem. The clean room therefore represents something interesting from a cyber perspective. Physically, the satellite may be extraordinarily controlled. Personnel wear protective equipment. Components are inspected. Environmental conditions are monitored. Hardware undergoes extensive testing.
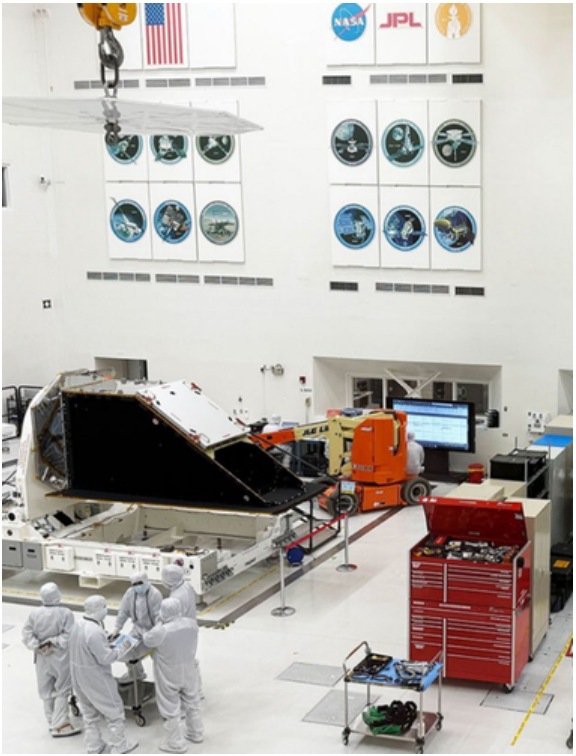
Figure 7: NASA’s NEO Surveyor and ASTHROS Clean Room NASA
Summary
But cybersecurity asks a different set of questions, such as: Who wrote the code?; Where did the processor originate?; What libraries are embedded in the software?
There is an important distinction to make. Commercial technology is not inherently less secure than purpose-built technology. COTS components can be thoroughly evaluated, tested, hardened, monitored, and incorporated into secure architectures. Commercial development can also deliver cybersecurity improvements much faster than traditional acquisition processes. The concern is visibility and assurance.
As the number of suppliers, software packages, components, interfaces, and external services grows, understanding exactly what is inside a system—and what it depends upon—becomes harder.
NIST’s commercial satellite cybersecurity guidance makes the broader point: commercial space is now part of an increasingly important infrastructure ecosystem, and cyber risk must be managed alongside the other risks inherent to operating in space. Commercialization, therefore, produces a paradox: The same technologies that make space faster, cheaper, and more accessible can also make the digital supply chain larger, more interconnected, and more difficult to fully understand.
Special Edition: The ISR Debrief Goes Behind The Integrity Flash The team behind The Integrity Flash has launched The ISR Debrief, a podcast focused on intelligence, targeting, military operations, space, and national security. Each episode
Special Edition: The ISR Debrief Goes Behind The Integrity Flash
The team behind The Integrity Flash has launched The ISR Debrief, a podcast focused on intelligence, targeting, military operations, space, and national security. Each episode brings together experienced operators, analysts, and practitioners to discuss the developments shaping today’s security environment.
Watch the special edition here
Prefer audio? The ISR Debrief is available on all major podcast platforms.
When Space Power Is Attacked on the Ground
This special edition of The ISR Debrief is built directly on reporting published in Flash Lite 151.1, specifically Alison Sayer’s article,”Ukraine Strikes Russia’s Progress Rocket and Space Centre.”
The discussion begins with Ukraine’s strike against one of Russia’s most important rocket production facilities, the factory responsible for producing much of the Soyuz launch vehicle family. From there, the conversation expands into a broader question that sits at the heart of modern space operations: Are we too focused on protecting satellites while overlooking the infrastructure that makes space power possible?
The Team Behind the Analysis
Joining host Chad Hartman are three of the primary authors behind The Integrity Flash:
Greg Gillinger, creator of The Integrity Flash and Senior Vice President for Strategy & Development at Integrity ISR
Alison Sayer, Air Force veteran and strategic analyst focused on space security and counterspace threats
Ron Lerch, retired Space Force Chief Master Sergeant with more than two decades of experience in space and counterspace intelligence
Together, they explore the same themes readers have seen developing across recent editions of The Integrity Flash.
Topics Discussed
This special episode explores:
The discussion expands well beyond satellites themselves and examines how launch facilities, production centers, communications infrastructure, logistics networks, and supply chains may become strategic targets in future conflicts.
A Key Takeaway
For decades, most discussions about space security focused on spacecraft in orbit. The panel argues that future conflicts may look very different.
As recent events in Ukraine and the Middle East suggest, adversaries may increasingly focus on targeting the supporting infrastructure that enables access to space in the first place. Factories, launch sites, communications networks, logistics systems, and industrial capacity may prove just as important as the satellites they support.
As Chad Hartman summarizes during the episode:
“Space power does not begin in orbit. It begins on the ground.”
Join the Conversation
If you enjoy this type of analysis:
Share this episode with others interested in space, intelligence, and national security.
Subscribe to The ISR Debrief on your preferred podcast platform.
Subscribe to The Integrity Flash to receive the written analysis that inspires these discussions.
Watch the Special Edition of The ISR Debrief: https://www.youtube.com/watch?v=H-Xm7fs6OGE
Audio version available on all major podcast platforms.
“The LINK spacecraft, which failed in its mission to rescue the SWIFT observatory, reentered at 1438 UTC Sep 24 over the S Pacific on a track from Tonga towards French Polynesia” ( @planet4589 via X) Congratulations to Dan Oltrogge, COMSPOC
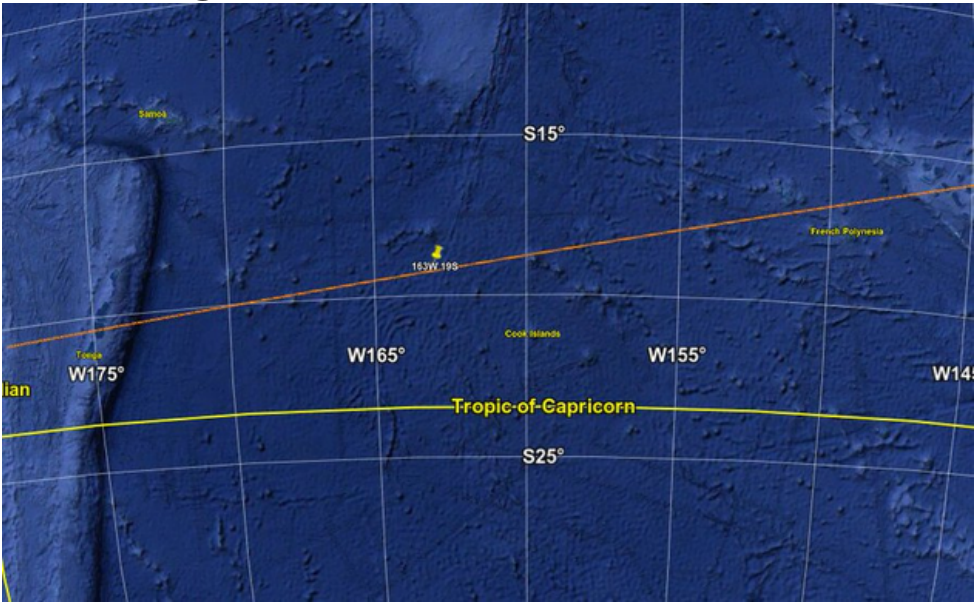
“The LINK spacecraft, which failed in its mission to rescue the SWIFT observatory, reentered at 1438 UTC Sep 24 over the S Pacific on a track from Tonga towards French Polynesia” (@planet4589 via X)
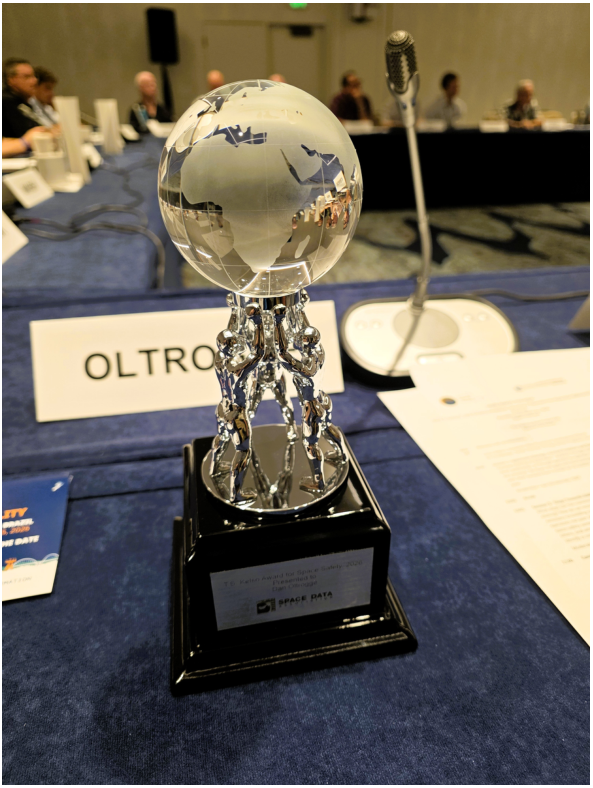
Congratulations to Dan Oltrogge, COMSPOC chief scientist and director of the Center for Space Standards and Innovation (and Friend of the Flash), on receiving the 2026 T.S. Kelso (also a Friend of the Flash) Space Safety Award. (space.com)
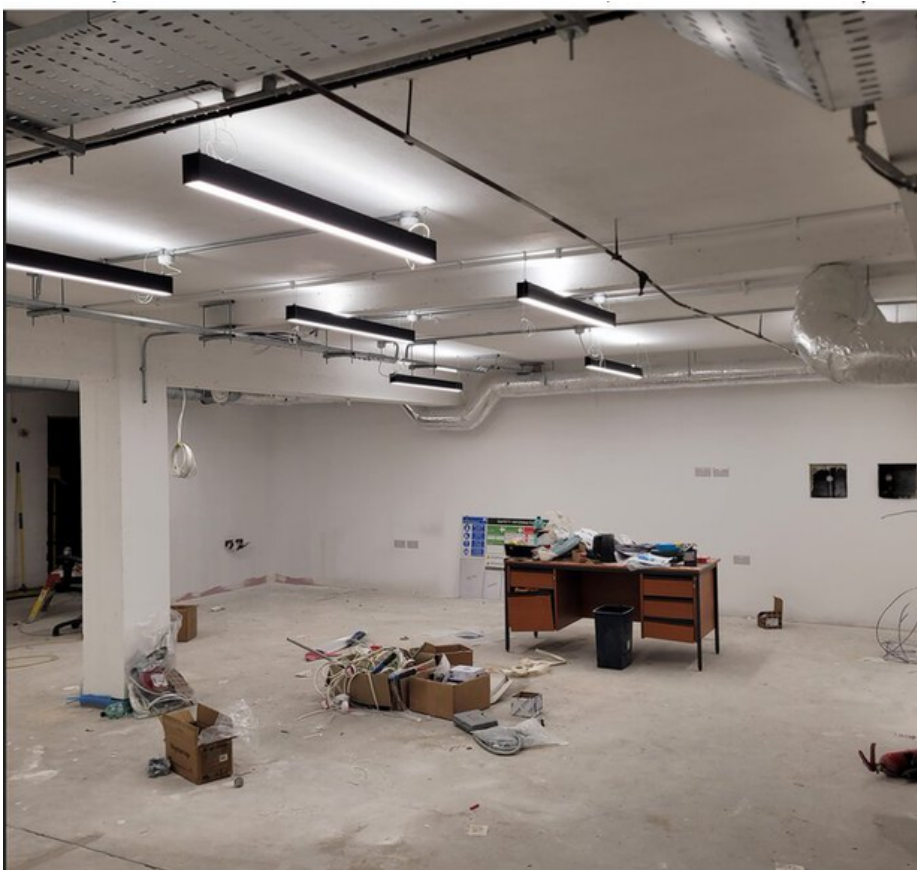
Jonathan’s Space Library finally has electricity! The lights went on today. The books should arrive in a few weeks. Interested in supporting? Head to https://www.gofundme.com/f/fund-jonathans-space-report-library-transition
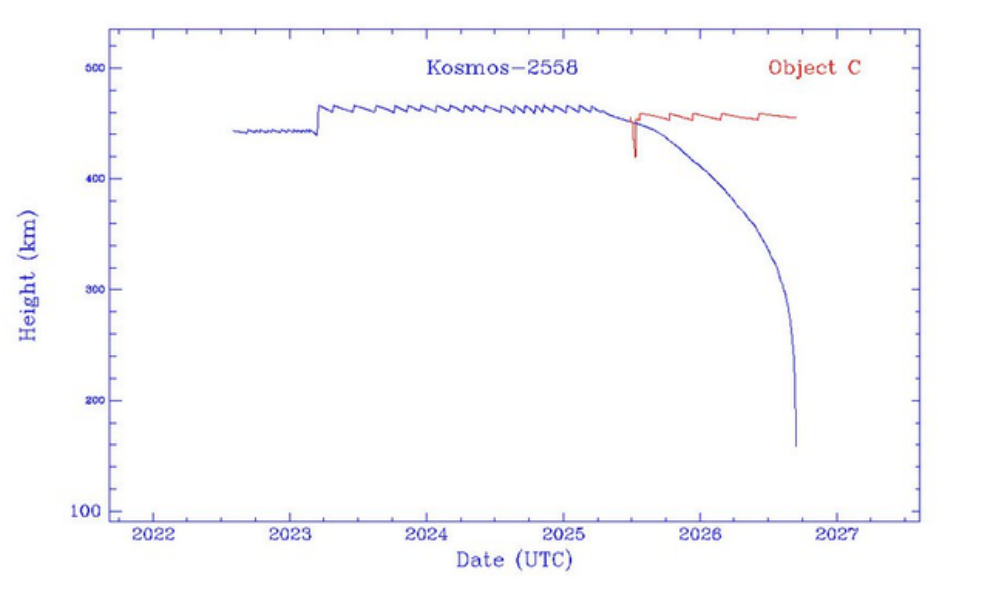
“Russia’s Nivelir-class military satellite Kosmos-2558 stopped orbit maintenance in Apr 2025; it reentered today, Sep 12. In Jun 2025 an object apparently released from it (“Object C”) was cataloged and begin making orbit reboost burns, which continue today” (@plante4589 via X)
Flash Insider
Subscribe to unlock full access to this Issue and the complete Flash archive.
Subscribe Now Already Subscribed? Log In « BackInsider feature
Download any issue or article as a brief-ready PDF or clean HTML. Become a Flash Insider to unlock exports and the full archive.
See Insider plans Already an Insider? Log in